Tagged: privilege escalation
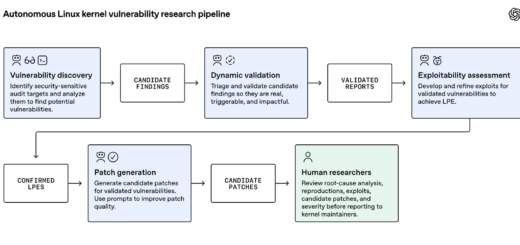
OpenAI recently deployed an autonomous artificial intelligence system to audit core open-source operating software. Specifically, the autonomous framework uncovered 948 unique Linux kernel vulnerabilities capable of achieving root privilege escalation. The intensive ten-day research...
TL;DR Docker released Docker Desktop version 4.98.0 on November 3, 2026. The release resolves two critical Docker Desktop vulnerabilities in container runtimes. The worst flaw lets unprivileged containers break out of isolation on Windows...
A cascade of fourteen security flaws across Linux and FreeBSD opened dangerous pathways to root privileges. Specifically, these flaws facilitate container escapes, virtual machine breakouts, and remote kernel code execution. Furthermore, functional exploits already...
TL;DR A full write-up and exploit are now public for CVE-2026-23074, a Linux kernel privilege escalation flaw in the teql traffic-control scheduler. The use-after-free dates back to Linux 2.6.12, the start of the kernel’s...
Two Unknown Bugs Became Full Server Control Two unknown vulnerabilities turned the Zammad support system into an entry point with full control of the server. The Dutch Institute for Vulnerability Disclosure (DIVD) revealed the...
The boundary separating an individual client account from the entire server infrastructure within LiteSpeed Web Server Enterprise has proven alarmingly fragile. Recently, cPanel issued a stark warning regarding a critical privilege escalation vulnerability. Within...
The September Patch Tuesday became the largest security update release in Microsoft’s history. The company closed 966 vulnerabilities, two of which attackers had already wielded in real-world attacks. Previous records proved short-lived: in July,...
NVIDIA graphics cards employ specialized error-correcting memory capable of detecting and repairing random data corruption on its own. A new attack called GPUThor has demonstrated that even this protection can be circumvented, leading to...
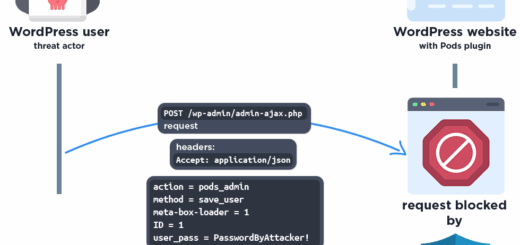
A WordPress site administrator’s password could be changed by an attacker without ever logging in. A critical vulnerability in the popular Pods plugin allowed an unauthenticated outsider to bypass several layers of security checks...
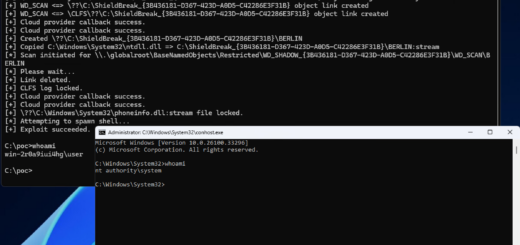
A Microsoft Defender vulnerability patched just one month ago appears to be exploitable once again. A researcher operating under the alias MSNightmare has published ShieldBreak – a new proof-of-concept that claims to bypass Microsoft’s...
Users of anonymous operating systems typically rely on the guarantee that no single program running within the environment can betray their true identity. Sometimes, however, a solitary flaw in the Linux kernel is sufficient...
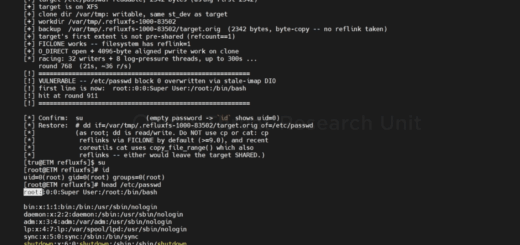
Unmasking the RefluXFS Vulnerability Impervious defense mechanisms in Linux offer no sanctuary when critical vulnerabilities manifest at the filesystem layer itself. The newly identified RefluXFS Linux vulnerability permits an unprivileged local actor to covertly...