Information Security News Blog
-
Malicious actors began exploiting a newly disclosed secure shell flaw in less than nine hours. Specifically, threat groups targeted the critical OpenSSH SSHole vulnerability across global internet infrastructure. Researchers confirmed active penetration attempts against...
-
Researchers recently discovered five zero-day vulnerabilities within the popular Ashlar-Vellum Cobalt computer-aided design software. Specifically, these critical flaws allow attackers to execute arbitrary code by manipulating complex drawing files. The Zero Day Initiative published...
-
Security researchers recently uncovered three vulnerabilities affecting the Philips Hue Bridge Pro smart lighting controller. Specifically, these flaws allow remote adversaries to compromise internal system processes completely. Attackers can chain authentication bypasses directly into...
GrapheneOS developers recently published a substantial software release for supported Google Pixel smartphones. Specifically, build 2026110700 delivers critical privacy enhancements, refined location controls, and vital kernel repairs. Furthermore, the firmware overhaul addresses hardware compatibility...
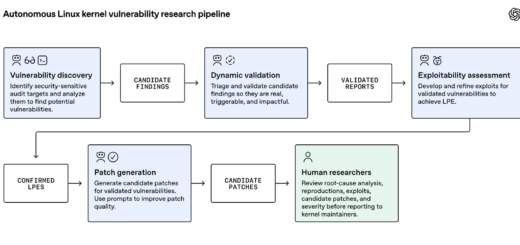
OpenAI recently deployed an autonomous artificial intelligence system to audit core open-source operating software. Specifically, the autonomous framework uncovered 948 unique Linux kernel vulnerabilities capable of achieving root privilege escalation. The intensive ten-day research...
A ubiquitous Chinese character utility recently became an unwitting vector for covert cyber espionage. Specifically, advanced threat actors hijacked network traffic to deploy the pervasive DarkVigil spyware framework. The malicious intrusion exploited unencrypted update...
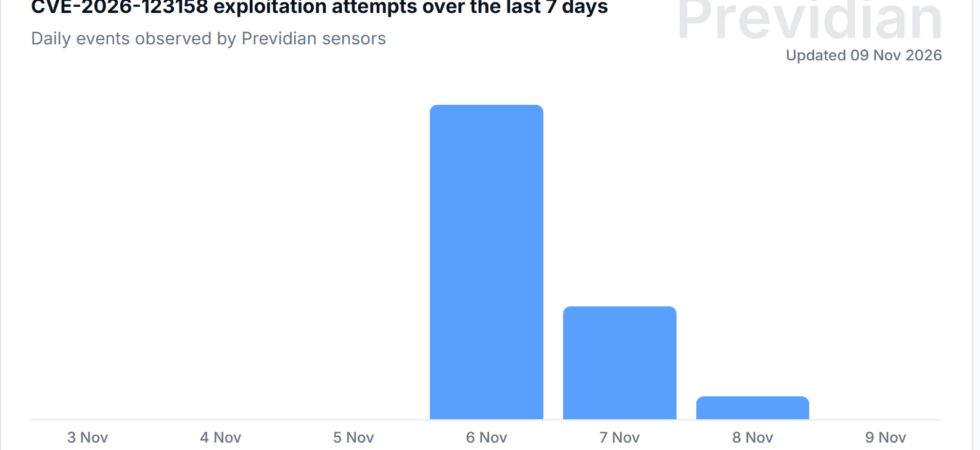
The OpenSSH development team published an urgent security maintenance release. Specifically, this update mitigates a critical OpenSSH password bypass issue. Tracked as CVE-2026-123158, the defect allows remote attackers to circumvent authentication checks using invalid...
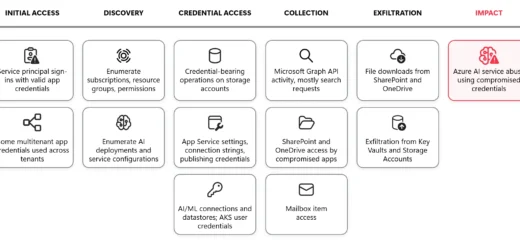
TL;DR Microsoft researchers discovered that threat actors are running an agentic AI offensive framework to locate exposed credentials in public GitHub repositories. In one observed case, an autonomous tool moved from scanning code to...
Adversaries recently breached the core infrastructure supporting prominent Web3 provider Chainstack. Specifically, the intruders penetrated internal environments and accessed sensitive customer databases containing cryptographic password hashes. Furthermore, executive leadership attributes this intrusion to an...
Adversaries recently breached internal systems at corporate identity provider WorkOS. Specifically, the intruders deployed an autonomous artificial intelligence tool known as ARTEX. The security compromise exposed enterprise customer directories and internal support correspondence. Consequently,...
TL;DR Better Auth published three security advisories on November 3, 2026, alongside version 1.7.16 of the TypeScript authentication library. The worst of these Better Auth vulnerabilities, rated CVSS 9.1, lets an unauthenticated attacker sign...
TL;DR Docker released Docker Desktop version 4.98.0 on November 3, 2026. The release resolves two critical Docker Desktop vulnerabilities in container runtimes. The worst flaw lets unprivileged containers break out of isolation on Windows...
TL;DR Elastic released new security updates on November 3, 2026. The advisories fix 12 Elastic security vulnerabilities across Elasticsearch, Kibana, APM Server, and Beats. These flaws allow traffic snooping, denial of service, and resource...
Fraudulent cryptographic certificates proliferated across the internet mere hours after researchers disclosed a severe certificate authority defect. Specifically, the catastrophic eMudhra certificate flaw enabled adversaries to reconstruct private cryptographic keys in fractions of a...
Canonical published an urgent advisory warning users of a critical security defect in LXD and MicroCloud. Specifically, this severe Canonical LXD vulnerability allows remote actors to bypass authentication protocols completely. Attackers who can reach...