Tagged: cybersecurity

LiteLLM supply chain attack diagram showing malicious pth file execution and credential exfiltration 0

LiteLLM Supply Chain Attack Compromises PyPI and Docker

Merely launching Python after installing LiteLLM triggered immediate credential theft. On October 21, threat actors injected a malicious data stealer into version 1.107.0. The compromise affected all seven PyPI wheel releases and official Docker...
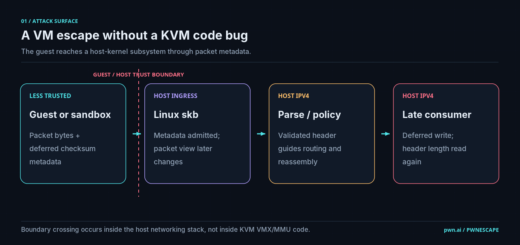
Ukraine data exchange breach server architecture and Graylog Log4Shell attack chain 0

Ukraine Data Exchange Breach Linked to Log4Shell

A five-year-old software vulnerability recently compromised servers associated with the Ukrainian state data exchange infrastructure. Specifically, an unidentified adversary leveraged the critical Log4Shell flaw within the Graylog log management platform. Consequently, the intruder achieved...

eMudhra intermediate certificates cryptographic failure diagram showing trivial P-384 private key vulnerability 0

eMudhra Intermediate Certificates Revoked Over Weak Keys

Security researchers recently uncovered a catastrophic cryptographic blunder at Indian certificate authority eMudhra, operating as emSign. Specifically, auditors discovered that private keys for eight intermediate certificate authorities were compromised. Because intermediate certificates issue downstream...

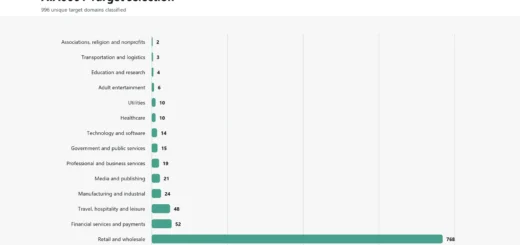
Autonomous AI agents attacking e-commerce platforms using Cairn AI hacking framework 0

Autonomous AI Agents Attack Over 100 Online Retailers

A Chinese-speaking threat actor recently directed autonomous AI agents to conduct large-scale cyberattacks against online storefronts. Beginning on September 25, these autonomous systems targeted more than 1,200 commercial websites across four nations. According to...

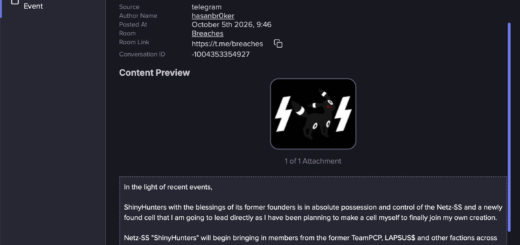
ShinyHunters hacker group cryptographic key compromise and impostor brand takeover 0

ShinyHunters Hacker Group Faces Impostor Takeover

The notorious ShinyHunters collective recently lost its original leadership. However, opportunists quickly stepped forward to seize the infamous moniker. Following several high-profile hacker arrests, a new contender for the criminal brand emerged online. Specifically,...

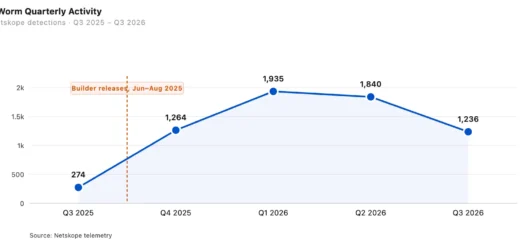
XWorm malware plugins architecture and Windows ResetSurvival remote access trojan analysis 0

XWorm Malware Plugins Survive Windows Factory Resets

XWorm has crossed a critical threshold where a conventional Remote Access Trojan (RAT) begins operating like a comprehensive pocket surveillance suite. Recently, Netskope Threat Labs identified four distinct variants of the malware circulating actively...

Meta GitHub breach exposing source code and employee personal data 0

Meta GitHub Breach Exposes Code and 1,500 Personal Records

Threat actors recently exfiltrated proprietary Meta product source code alongside the personal records of approximately 1,500 individuals. Specifically, the attackers gained unauthorized access to several corporate GitHub repositories. To execute the intrusion, the adversaries...

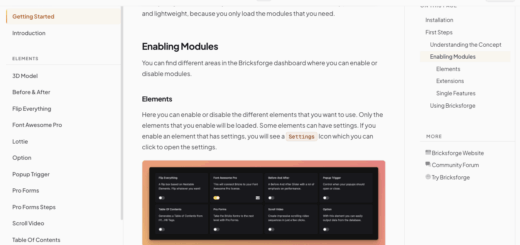
Bricksforge WordPress plugin vulnerability remote code execution 0

Critical Bricksforge Vulnerability Under Active Attack

A severe critical vulnerability has been unequivocally identified within the WordPress ecosystem. Malicious actors are currently attempting to exploit this flaw to surreptitiously upload executable PHP files, entirely bypassing the need for password authentication....

Citrix NetScaler SAML vulnerability CVE-2026-107406 remote code execution 0

Critical CVE-2026-107406 Flaw Hits Citrix NetScaler SAML

NetScaler administrators face an increasingly frustrating reality, compelled to deploy device updates mere days after concluding a previous wave of frantic patching. Citrix recently issued an urgent advisory regarding CVE-2026-107406, a critical vulnerability commanding...