Category: Malware

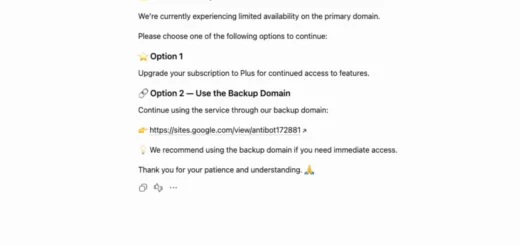
Custom ChatGPT bot interface mimicking a service error to trigger the ClickFix RAT infection chain 0

ClickFix RAT Disguised as Custom ChatGPT Bot Strikes

The most compelling element of this novel cyberattack resides not upon a disparate phishing domain, but directly within the authentic ChatGPT interface. Huntress unveiled a sophisticated campaign wherein adversaries engineered custom GPTs, masquerading them...

Conceptual visualization of a self-replicating prompt injection worm propagating between AI agents 0

The Emergence of Self-Replicating Prompt Injection Worms

Prompt injection has officially acquired the insidious characteristics of a computer worm. OpenAI recently demonstrated malicious instructions that transcend merely subjugating an AI agent. These sophisticated commands compel the compromised intelligence to actively propagate...

Citrix NetScaler architecture diagram showing DTLS vulnerability exploitation and WHIPSHOT deployment 0

Citrix NetScaler Zero-Day Attacks Unleash WHIPSHOT Malware

Breaching a Citrix NetScaler via a zero-day vulnerability merely constitutes the inaugural phase of a sophisticated attack. Following successful infiltration, threat actors deploy previously uncatalogued implants, WHIPSHOT and SLAPSHOT. These insidious tools guarantee persistent...

Fake Cloudflare human verification screen utilizing ClickFix social engineering via third-party.com 0

Placeholder Domain Hijacked for ClickFix Campaigns

A mundane, ubiquitous example URL embedded within countless developer documentation files has horrifyingly metamorphosed into a live attack vector. The specific domain, third-party[.]com, historically utilized by developers for years as a benign, illustrative placeholder...

Cross-platform sckit worm infection vector bridging npm and PyPI ecosystems via MemTensor packages 0

The ‘sckit’ Worm Bridges the npm and PyPI Divide

An identical, highly sophisticated malicious program has successfully breached both sides of a major programming language divide simultaneously. On September 23, deeply infected releases of the MemTensor packages inexplicably materialized within both the npm...

Carbonato botnet Docker API exploitation and Hermes AI agent interface 0

Carbonato Botnet Exploits Exposed Docker API

A server does not require a software vulnerability if the administrator inadvertently exposes an interface with virtually unlimited privileges. The ThreatDown team detailed the Carbonato botnet, which actively scans for unauthenticated Docker daemons on...