Tagged: malware

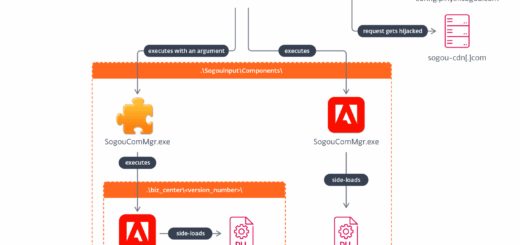
Sogou Input Method malware diagram illustrating DNS hijacking and DarkVigil spyware delivery mechanisms 0

Sogou Input Method Malware Delivers DarkVigil Spyware

A ubiquitous Chinese character utility recently became an unwitting vector for covert cyber espionage. Specifically, advanced threat actors hijacked network traffic to deploy the pervasive DarkVigil spyware framework. The malicious intrusion exploited unencrypted update...
Fake Arch Linux packages posing as yay and paru in the AUR, running a root shell script in a yay paru malware campaign 0

Fake yay and paru Packages Hit Arch Linux AUR

Counterfeit AUR Helpers Run Code as Root Researchers found fake Arch Linux packages that pose as the popular tools yay and paru. During installation, they run malicious code with root privileges. The attackers kept...

XWorm malware plugins architecture and Windows ResetSurvival remote access trojan analysis 0

XWorm Malware Plugins Survive Windows Factory Resets

XWorm has crossed a critical threshold where a conventional Remote Access Trojan (RAT) begins operating like a comprehensive pocket surveillance suite. Recently, Netskope Threat Labs identified four distinct variants of the malware circulating actively...

Fake Cloudflare human verification screen utilizing ClickFix social engineering via third-party.com 0

Placeholder Domain Hijacked for ClickFix Campaigns

A mundane, ubiquitous example URL embedded within countless developer documentation files has horrifyingly metamorphosed into a live attack vector. The specific domain, third-party[.]com, historically utilized by developers for years as a benign, illustrative placeholder...

Fake Cloudflare CAPTCHA ClickFix interface leading to Psychedelic Stealer installation 0

Psychedelic Stealer Weaponizes Compromised Websites

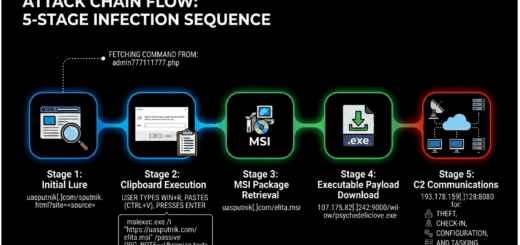
A perilous trap may now await visitors upon seemingly familiar digital terrain: malicious actors have systematically compromised several legitimate Ukrainian websites, covertly embedding a fraudulent Cloudflare verification gateway. This deceptive interface cunningly orchestrates the...

Windows Update screen showing KB5124008 and AMD Radeon graphics card 0

Windows Update KB5124008 Triggers AMD Radeon Chaos

The September Windows 11 update, specifically KB5124008, is now heavily associated with a fresh wave of severe system failures on computers equipped with AMD Radeon graphics cards. Users running Windows 11 versions 24H2 and...

REVSTEALER malware components architecture and infostealer infection process 0

The Hidden Perils of REVSTEALER Infections

Eradicating a data stealer from a computer does not mean the system is safe. The cybersecurity firm Elastic has outlined four previously unknown components linked to the REVSTEALER credential harvesting infostealer. Unlike the primary...

Pegasus spyware in Serbia forensic report detailing Pegasus spyware infections 0

Pegasus Spyware in Serbia Targets Student Activist

TL;DR Researchers at the Citizen Lab and the SHARE Foundation confirmed a mercenary spyware attack in Serbia. A zero-click exploit delivered Pegasus spyware to an iPhone belonging to a pro-democracy student activist. Meanwhile, independent...

A conceptual illustration of a hacker exploiting Microsoft Teams to gain unauthorized remote access to a corporate network. 0

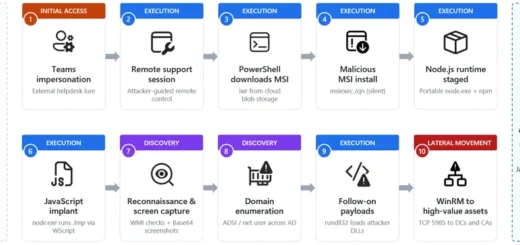
Teams Phishing Targets Enterprise Access

An unexpected request originating from corporate technical support frequently appears entirely innocuous. This perception persists until an employee unwittingly surrenders computer control directly to an unknown individual. Microsoft recently exposed a highly active campaign...

A conceptual image of a deceptive software download mimicking legitimate applications 0

Deceptive Software Campaign Exposed

A routine software search recently transformed into a critical entry point for severe malware infections. Microsoft recently exposed a sophisticated counterfeit installer campaign. Participants in this operation meticulously cloned the websites of renowned software...