The core maintenance team behind the Ruby programming language has released versions 4.0.9, 3.4.12, and 3.3.13. Specifically, these critical updates resolve severe vulnerabilities within the embedded Onigmo regular expression parsing engine. These underlying memory...
A Forgotten Backdoor on Millions of PCs An abandoned build of Popcorn Time kept a dangerous mechanism on millions of computers for years. Through it, anyone could quietly run code with top system privileges....
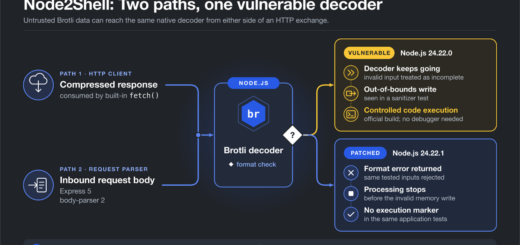
A critical flaw within Google’s Brotli compression algorithm has sent shockwaves through the software industry. Specifically, the Brotli CVE-2026-111497 vulnerability permits unauthenticated attackers to corrupt server memory remotely. Security researchers have already demonstrated practical...
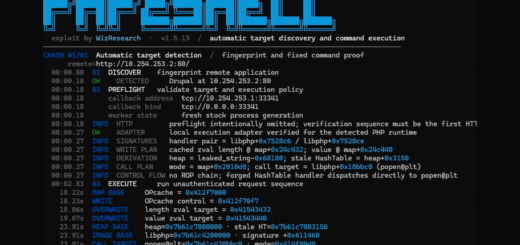
Researchers have engineered a reliable exploit against critical memory safety protections. Specifically, cybersecurity analysts at VulnCheck defeated Address Space Layout Randomization (ASLR) on modern 64-bit systems. Their technical breakthrough transforms the dangerous PHP2Shell vulnerability...
The PHP Foundation recently published a security disclosure detailing a remote code execution risk. Specifically, maintainers registered the issue as CVE-2026-115560 across national vulnerability databases. However, developers opted against deploying an immediate emergency point...
The Zero Day Initiative (ZDI) team at Trend Micro recently experienced an operational mishap. Specifically, researchers inadvertently copied several confidential vulnerability reports to the public Linux Kernel Mailing List. Among these disclosures were two...
A Home Media Server Turns Into a Botnet Node An ordinary home media server can become a tool for cryptocurrency mining and for hidden relaying of other people’s traffic. Researchers found a chain of...
The PHP security team recently issued an urgent alert across the web ecosystem. Specifically, maintainers scheduled an expedited update on Wednesday, 21 October 2026 at 14:00 UTC to remediate two severe flaws. Although officials...
GitLab Patches a Maximum-Severity Flaw GitLab has fixed a critical vulnerability that, under certain conditions, lets attackers run arbitrary code on a server. They need no password and no user interaction. The flaw received...
Attackers Need No Password The latest attacks on Citrix NetScaler require no password at all. Citrix has disclosed two critical zero-day flaws in NetScaler ADC and NetScaler Gateway. Attackers can strike corporate VPNs and...
A single link in an attacker’s hands can make WordPress install a theme without a button being pressed, provided an already-authenticated administrator opens it. On September 17, WordPress released version 7.1.1, which closes a...