Tagged: threat intelligence
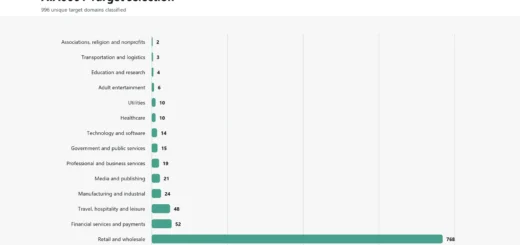
A Chinese-speaking threat actor recently directed autonomous AI agents to conduct large-scale cyberattacks against online storefronts. Beginning on September 25, these autonomous systems targeted more than 1,200 commercial websites across four nations. According to...
The notorious ShinyHunters collective recently lost its original leadership. However, opportunists quickly stepped forward to seize the infamous moniker. Following several high-profile hacker arrests, a new contender for the criminal brand emerged online. Specifically,...
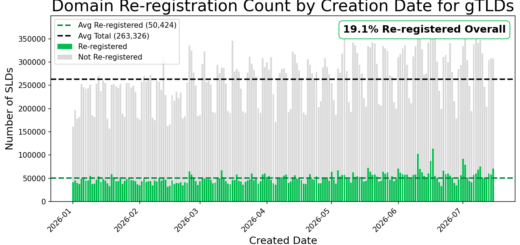
An old address on the internet can appear far more trustworthy than a brand-new one – even after its original owner has long since abandoned it. In a series of reports, researchers at Infoblox...
Google is introducing a unified naming system for the hacker groups its specialists track. Instead of labels like APT1 and a jumble of unrelated identifiers, attackers will now receive memorable two-word aliases. The transition...
The Funky Mantis extortion group has transformed an ordinary file-encryption toolkit into a fully fledged commercial service. Members now manage affiliates, sell access to compromised networks, and oversee negotiations with victims. Researchers have found...
From Assistant to Orchestrator Artificial intelligence no longer merely whispers isolated commands to hackers. Instead, it orchestrates nearly the entire assault. It manages everything from pinpointing vulnerabilities to traversing networks and exfiltrating data. Recently,...
The tiny image beside a browser tab reveals surprisingly profound server details. A resourceful security expert engineered a brilliant artificial intelligence framework. This system scrutinized millions of website favicons. Subsequently, it transformed these seemingly...
Even services built for private conversation sometimes betray themselves. The giveaway is not the content of the messages. Instead, it is the ordinary network infrastructure behind them. Analysts at Covert Security found that the...
For two decades, the underground forum XSS reigned as a premier sanctuary for cybercriminals. Inside this digital enclave, actors routinely recruited accomplices and bartered illicit access. Furthermore, users frequently debated malware architectures, phishing methodologies,...
The ransomware landscape is undergoing a period of significant consolidation as major syndicates reassert their dominance. After two years characterized by fragmentation and the emergence of myriad minor actors, the cybercriminal underworld is swiftly...
The Iranian threat collective Seedworm maintained a clandestine presence within the infrastructure of a prominent South Korean electronics manufacturer for nearly a week. During this tenure, the adversaries systematically harvested telemetry, purloined credentials, and...
In a seminal transgression, adversaries have endeavored to compromise municipal water infrastructure by wielding the sophisticated cognitive capabilities of modern neural networks. During a targeted offensive against the municipal water supply of Monterrey, Mexico,...