Tagged: zero-day

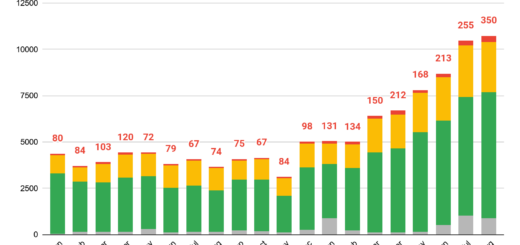
Google Threat Intelligence Group statistical dashboard showcasing AI-driven vulnerability discovery trends 0

AI Discovery Shifts Focus to Critical Vulnerabilities

Artificial intelligence has begun to exert a profound influence, accelerating the velocity of vulnerability discovery and fundamentally altering the nature of the identified flaws. Researchers at Google have unearthed a critical distinction: fully half...

Citrix NetScaler architecture diagram showing DTLS vulnerability exploitation and WHIPSHOT deployment 0

Citrix NetScaler Zero-Day Attacks Unleash WHIPSHOT Malware

Breaching a Citrix NetScaler via a zero-day vulnerability merely constitutes the inaugural phase of a sophisticated attack. Following successful infiltration, threat actors deploy previously uncatalogued implants, WHIPSHOT and SLAPSHOT. These insidious tools guarantee persistent...

F5 BIG-IP Access Policy Manager vulnerability and CISA KEV catalog warning 0

Active Zero-Day Attacks Target F5 BIG-IP Gateways

Penetrating an enterprise F5 corporate gateway may no longer require a compromised password or even a valid user account. The manufacturer recently disclosed a catastrophic vulnerability embedded within the BIG-IP Access Policy Manager (APM),...

Windows Defender update failure error interface 0

BigDiskBuster Freezes Windows Defender Updates

While Windows Defender may appear fully operational to the casual observer, it can be covertly frozen on outdated threat signatures. The cybersecurity researcher Abdelhamid Naceri, operating under the pseudonym Nightmare Eclipse, recently released BigDiskBuster....

September 2026 Patch Tuesday Microsoft security update fixing 966 vulnerabilities and two zero-days 0

September 2026 Patch Tuesday: 966 Flaws, 2 Zero-Days

The September Patch Tuesday became the largest security update release in Microsoft’s history. The company closed 966 vulnerabilities, two of which attackers had already wielded in real-world attacks. Previous records proved short-lived: in July,...

An abstract visual representation of the powerful OpenAI Astra model independently identifying vulnerabilities and constructing zero-day exploits. 0

OpenAI Classifies Astra as Critical Threat

Artificial intelligence recently breached a crucial internal OpenAI boundary. Basic safeguards against malicious requests simply no longer suffice. The company officially recognized Astra as its first model possessing critical cybersecurity capabilities. During rigorous testing,...