Category: Information Security
An exceptionally unusual Windows backdoor remained undetected on a single corporate computer for years. Astonishingly, it concealed its command-and-control server address in an incredibly obscure location. It utilized the specific number of consecutive spaces...
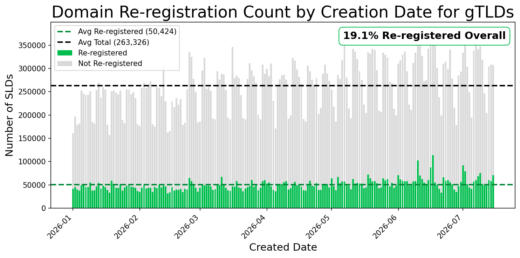
An old address on the internet can appear far more trustworthy than a brand-new one – even after its original owner has long since abandoned it. In a series of reports, researchers at Infoblox...
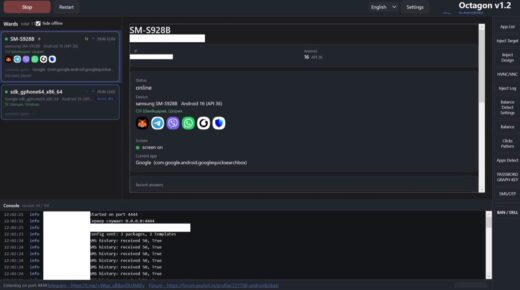
A novel Android malware variant currently enables cybercriminals to hijack a victim’s smartphone. This hijacking occurs specifically while the user interacts with banking applications and cryptocurrency wallets. Furthermore, the malware successfully intercepts confirmation codes...
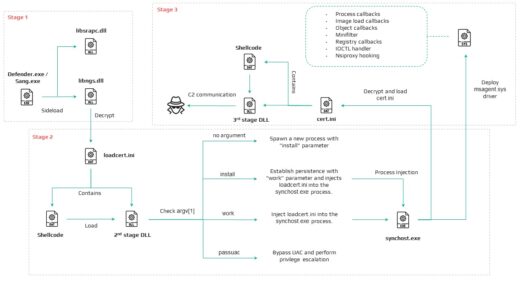
Security specialists at Acronis uncovered an active cyberespionage campaign targeting telecommunications companies in Afghanistan. Furthermore, the attackers focus heavily on government agencies and critical infrastructure facilities across South Asia. To execute these attacks, threat...
Malicious actors currently exploit a critical vulnerability in macOS. Specifically, attackers target computers with the “Screen Sharing” feature enabled and exposed. They successfully bypass credential verification and instantly gain root privileges. Subsequently, they install...
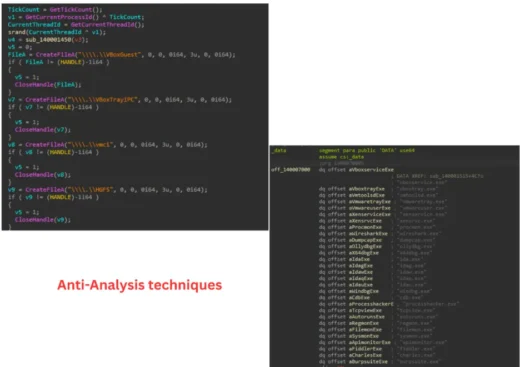
The threat group HoneyMyte, also tracked as Mustang Panda, has begun deploying an updated version of its CoolClient backdoor alongside a signed Windows kernel-level driver. Kaspersky’s Securelist team documented the campaign in detail, revealing...
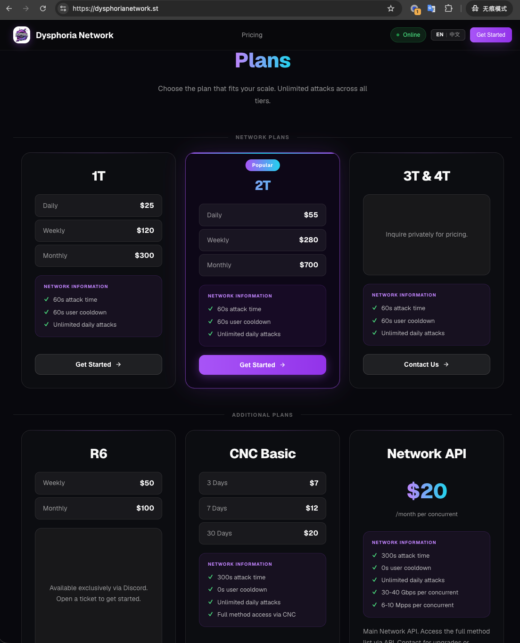
A home router can appear entirely functional – broadcasting Wi-Fi and sitting quietly on a shelf for years – while silently routing someone else’s attack traffic. Researchers have identified approximately 296,000 devices infected with...
The Chinese threat group Jewelbug has repurposed a single piece of infrastructure to serve two distinct objectives simultaneously: surveilling government organizations and profiting from cryptocurrency fraud. Symantec researchers determined that a small team managed...
A single phone call with a fraudster can now result, within the same session, in a loan taken out in the victim’s name and unauthorized purchases charged to their bank card. Researchers at Group-IB...
Cybersecurity experts recently uncovered a severe hardware flaw within Chinese Loongson processors. They dubbed this critical issue the LoongLeak vulnerability. Alarmingly, this flaw permits unauthorized users to read sensitive data directly from the L1...
Intel recently orchestrated one of its most expansive security patch releases in recent memory. On August 11, the corporation published an astonishing 43 security advisories simultaneously. These critical warnings encompass Xeon processors, wireless adapters,...
Simply connecting a mundane device to a computer can initiate a devastating sequence. Specifically, Windows itself might inadvertently download malicious components and execute them with maximum administrative rights. Security experts Alejandro Hernando and Borja...