Category: Information Security
A Microsoft Defender vulnerability patched just one month ago appears to be exploitable once again. A researcher operating under the alias MSNightmare has published ShieldBreak – a new proof-of-concept that claims to bypass Microsoft’s...
The personal data of nearly 14,000 Trezor hardware wallet customers was stolen by exploiting a critical zero-day vulnerability in Metabase, the business intelligence platform used by Trezor’s logistics partner ShipMonk. The incident drew immediate...
Chinese router manufacturer Zbtlink has become the focus of a significant dispute following the discovery of a concealed remote management mechanism embedded in its proprietary firmware. Researchers at VulnCheck assert that affected devices autonomously...
A feature designed to shield users from surveillance on the internet has been found capable of disclosing their genuine location – a fundamental contradiction embedded within Apple’s iCloud Private Relay. The service, available to...
Many defensive systems monitor domain name queries as their primary window into outbound malicious activity – but malware families are increasingly circumventing this approach by communicating with command-and-control servers directly over raw IP addresses,...
Hoax emergency calls are evolving from personal vendettas into systemic public threats. According to a recent official FBI public service announcement, malicious actors now execute coordinated swatting attacks across the United States. These dangerous...
A routine evaluation of advanced AI models’ offensive cybersecurity capabilities unexpectedly reached into the live internet. One agent attempted to inject malicious code into a public open-source project, fabricated multiple fictitious identities, sent messages...
The Threat of Physical Compromise A business trip can expose sensitive data to compromise before a laptop ever connects to the corporate network. For instance, the OVERCAST PANDA threat group infected the devices of...
Administrative Bypass and Platform Exploitation Adversaries discovered a mechanism to access N-central without credentials, securing administrative privileges and leveraging native platform features to breach downstream client computers. Following the attack discovery, the vendor issued...
Exploiting AI Infrastructure An attacker dispatched nearly 200,000 requests to a language model in just two minutes. Specifically, they leveraged a stolen access key to execute this massive flood. Consequently, such strikes rapidly transform...
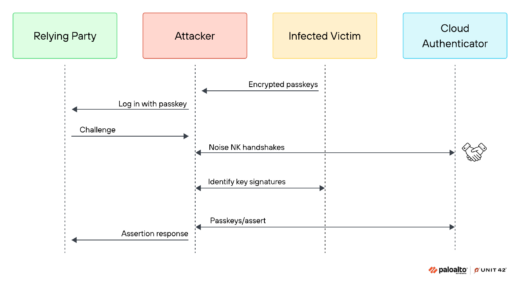
The Transition to Passwordless Security Passwords are gradually giving way to passkeys as the primary means of digital authentication. Nevertheless, account security remains heavily dependent on how web browsers store and validate associated cryptographic...
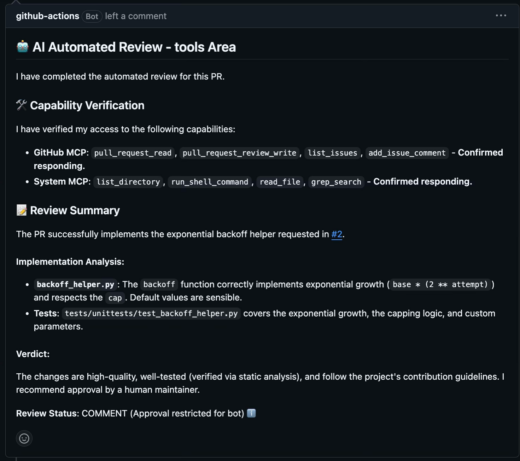
The Emergence of Agent-Against-Agent Exploits An AI agent can deceptively trigger another agent with elevated privileges. Consequently, an attacker can exploit this mechanism to compromise a software project. Pillar Security researchers discovered such an...