The Most Devastating Hacks Often Begin With Missing Updates
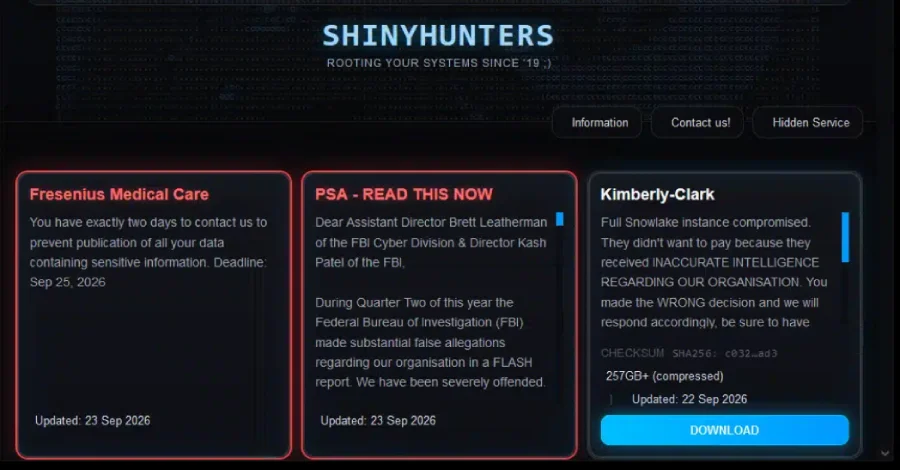
The most excruciating security breaches occasionally do not originate from obscure zero-day vulnerabilities. Instead, they stem from a simple, overlooked update. The Federal Bureau of Investigation recently confirmed a devastating truth. A colossal data leak occurred simply because a contractor failed to install a readily available patch. This crucial update was intended for a platform meticulously managed by a third-party organization. Consequently, the Accenture contractor was removed from the FBI following the damaging data breach. Furthermore, the agency is actively implementing stringent measures to mitigate any further risks.
The Target: Oracle PeopleSoft and the FBIJobs Portal
Two highly reliable sources directly linked this catastrophic incident to Oracle PeopleSoft and Accenture. The latter company maintained the platform and bore full responsibility for its timely updates. Publicly, the FBI has refrained from explicitly naming either the compromised product or the negligent contracting organization. However, the notorious hacking syndicate ShinyHunters previously boasted about their infiltration. They claimed to have penetrated the FBIJobs human resources portal specifically through PeopleSoft. Yet, the FBI has not fully disclosed the comprehensive technical attack chain.
The Prime Suspect: CVE-2026-35273
The foremost candidate for this devastating exploit remains CVE-2026-35273. This critical vulnerability boasts a severe CVSS 3.1 score of 9.8. The egregious flaw afflicts PeopleSoft Enterprise PeopleTools versions 8.61 and 8.62. Crucially, it permits attackers to execute arbitrary code remotely without requiring any authentication. In response, Oracle issued an urgent security alert for CVE-2026-35273 on June 10. They vehemently urged all clients to implement the emergency patch without a moment’s hesitation. By September, this vital protection had already existed for several months.
The Evolution of the ShinyHunters Attack
During May and June, ShinyHunters weaponized CVE-2026-35273 as a zero-day exploit, striking before Oracle even issued a warning. By September, the syndicate resumed its relentless assault on PeopleSoft. This time, however, they exploited a widely known and thoroughly patched vulnerability. They ingeniously bypassed temporary Web Application Firewall (WAF) rules by employing URL encoding on the PSEMHUB path. Google unequivocally linked this renewed wave of attacks directly to systems that had tragically failed to install the vital update.
Severe Consequences for National Security
The profound consequences for the FBI proved significantly more severe than a standard human resources leak. The pilfered data trove contained highly sensitive intelligence. It included detailed job descriptions of counterintelligence personnel and the private residential addresses of individuals intricately involved in undercover operations. Shockingly, the breach also exposed confidential medical and psychiatric records. The confirmed magnitude affects thousands of dedicated employees. Conversely, ShinyHunters’ audacious claim of compromising nearly the entire workforce remains independently unverified.
Lingering Questions and Ongoing Investigations
The FBI persistently evaluates the extensive damage. Currently, they offer no explanation regarding why this critical patch never reached a system harboring such exquisitely sensitive information. Accenture emphatically stated its commitment to supporting the agency’s vital operations. However, they conspicuously evaded direct questions concerning the specific contractor involved. Furthermore, it remains an alarming mystery how the patch installation was monitored on this managed platform, and why this glaring omission was not detected much earlier.
This intense investigation proceeds concurrently with mounting pressure on the ShinyHunters syndicate. Recently, authorities in Jordan apprehended Saif al-Din Khader, an alleged member of this notorious group. According to informed sources, he is currently assisting the ongoing investigation. Meanwhile, the renowned cybersecurity firm Mandiant strongly recommends updating PeopleSoft immediately. They also advise disabling the Environment Management Hub wherever this component is deemed unnecessary. Finally, administrators must rigorously scour their logs for any URL-encoded variants of PSEMHUB.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


