Category: Information Security
Attackers can force Microsoft Defender to delete its own security components using a native Windows driver. This technique affects systems from Windows 7 through Windows 11 25H2. It requires neither a software vulnerability exploit...
T-Mobile specialists were forced to literally cut a network cable to prevent hackers from penetrating the carrier’s infrastructure. The incident took place in 2024, during a large-scale espionage campaign that U.S. authorities have linked...
Victims of ransomware attacks are now facing an entirely new scheme: shortly after an attack, an unknown company reaches out, already aware of the stolen data, and offers – for a fee – to...
Over 100,000 educators globally fell victim to relentless hackers who spent years plundering academic research, proprietary books, and other invaluable intellectual property. The United States indicted 17 Iranian nationals affiliated with the Mabna Institute...
Security specialists at Zscaler have unearthed a novel backdoor dubbed C2Looper, which malicious actors presumably deploy as a precursor to devastating ransomware assaults. This pernicious software enables adversaries to establish a clandestine foothold within...
Hackers have begun exploiting a critical Windows vulnerability that allows remote code execution on a target computer without requiring an account or any user interaction whatsoever. The U.S. Cybersecurity and Infrastructure Security Agency (CISA)...
A single click on a maliciously crafted link was sufficient to trigger a severe data breach through Microsoft Copilot Personal. Astonishingly, without any further user interaction, the assistant would begin scanning connected emails, calendars,...
The Medusa threat group has attacked more than 500 U.S. critical infrastructure organizations since June 2021. As recently as February 2025, American authorities had counted just over 300 confirmed victims, meaning the roster of...
More than 50,000 Berlin households risk not receiving their housing benefit payments on time following a hacker attack on the city government’s information systems. The disruption has affected not only benefit payments, but also...
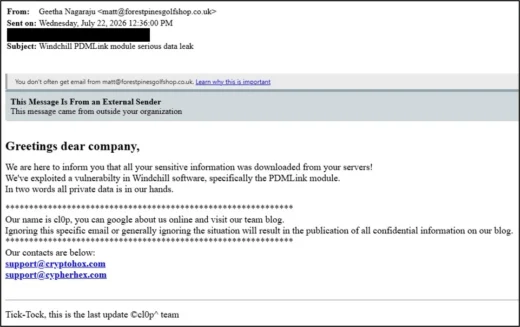
The Clop threat group is likely using a purpose-built web shell to steal data from PTC Windchill and FlexPLM servers. The malware is engineered specifically around Windchill’s internal architecture: it connects to the application...
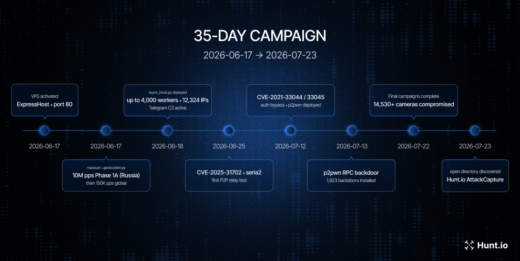
In a stunning display of cyber aggression, a lone operator successfully infiltrated over 14,500 Dahua security cameras within a mere five weeks. Alarmingly, the attacker meticulously planted a hidden backdoor account on nearly 2,000...
Malicious actors brazenly targeted developers utilizing counterfeit packages deployed simultaneously across two highly prominent repositories. Cybercriminals stealthily introduced 16 malicious libraries into RubyGems and strategically placed another 37 within the npm registry. They meticulously...