Tagged: Infosec

Hacker attacking a vulnerable Gitea server through an open registration portal 0

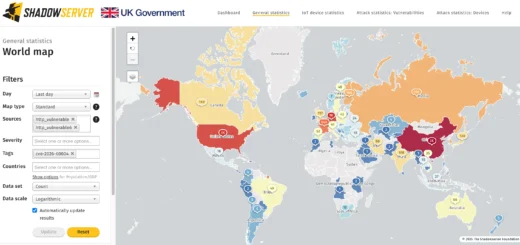
Critical Gitea RCE Vulnerability Under Attack

Open registration on developer platforms generally streamlines onboarding processes. However, concerning Gitea, this convenience inadvertently transformed a critical vulnerability into an easily accessible intrusion point. The Shadowserver Foundation recently identified a staggering 8,393 internet-facing...
Norway government digital services experiencing massive DDoS attack disruptions 0

Massive DDoS Attack Disrupts Norwegian Digital Services

For the third consecutive day, a massive Distributed Denial-of-Service (DDoS) attack continues to severely disrupt Norway’s state digital services. The overwhelming overload upon the shared infrastructure directly impacted critical authorization systems, electronic signatures, and...

Concept art demonstrating security by obsolescence with older tech evading hackers 0

Security by Obsolescence: When Older Tech Defeats Hackers

Occasionally, technological reliability hinges less upon inherent architectural age and more upon the fundamental lack of incentive for exploitation. Cybersecurity luminary Mikko Hyppönen eloquently identifies this fascinating phenomenon as “security by obsolescence.” Antiquated software...

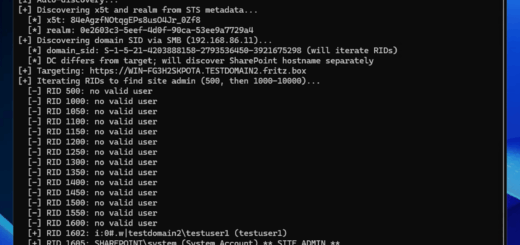
Microsoft SharePoint server security flaw diagram showing exploit chain 0

Critical Microsoft SharePoint Exploit Chain Exposed

Two distinct Microsoft SharePoint vulnerabilities have seamlessly merged to form a devastating, fully operational exploit chain. This formidable combination empowers malicious actors to execute arbitrary code remotely on a targeted server, completely bypassing the...

Hydra Remote malware operating a hidden desktop to steal active browser sessions 0

Hydra Remote Malware Hijacks Browser Sessions

The malicious software known as Hydra Remote empowers an attacker to generate a covert desktop environment on an infected computer. Crucially, this secondary workspace remains entirely invisible to the legitimate device owner. The attacker...

Apple Find My hack showing location tracking data on a Linux terminal interface 0

Apple Find My Hack: Location Tracking on Linux

An enterprising researcher successfully compelled Apple Find My to operate within an environment completely unsupported by the corporation. A 22-year-old security specialist, operating under the pseudonym Zerotistic, cleverly registered a Linux machine within Apple’s...

ToxicPanda Android banking trojan stealing PINs on a smartphone screen 0

ToxicPanda Android Banking Trojan: 2.0 Upgrade

The notorious banking trojan ToxicPanda has resurfaced in a significantly more formidable iteration. ToxicPanda 2.0 now possesses the capability to pilfer PINs from banking and cryptocurrency applications. It intercepts smartphone lock passwords with alarming...