Danfoss Controller Attack Hits Retail Refrigeration
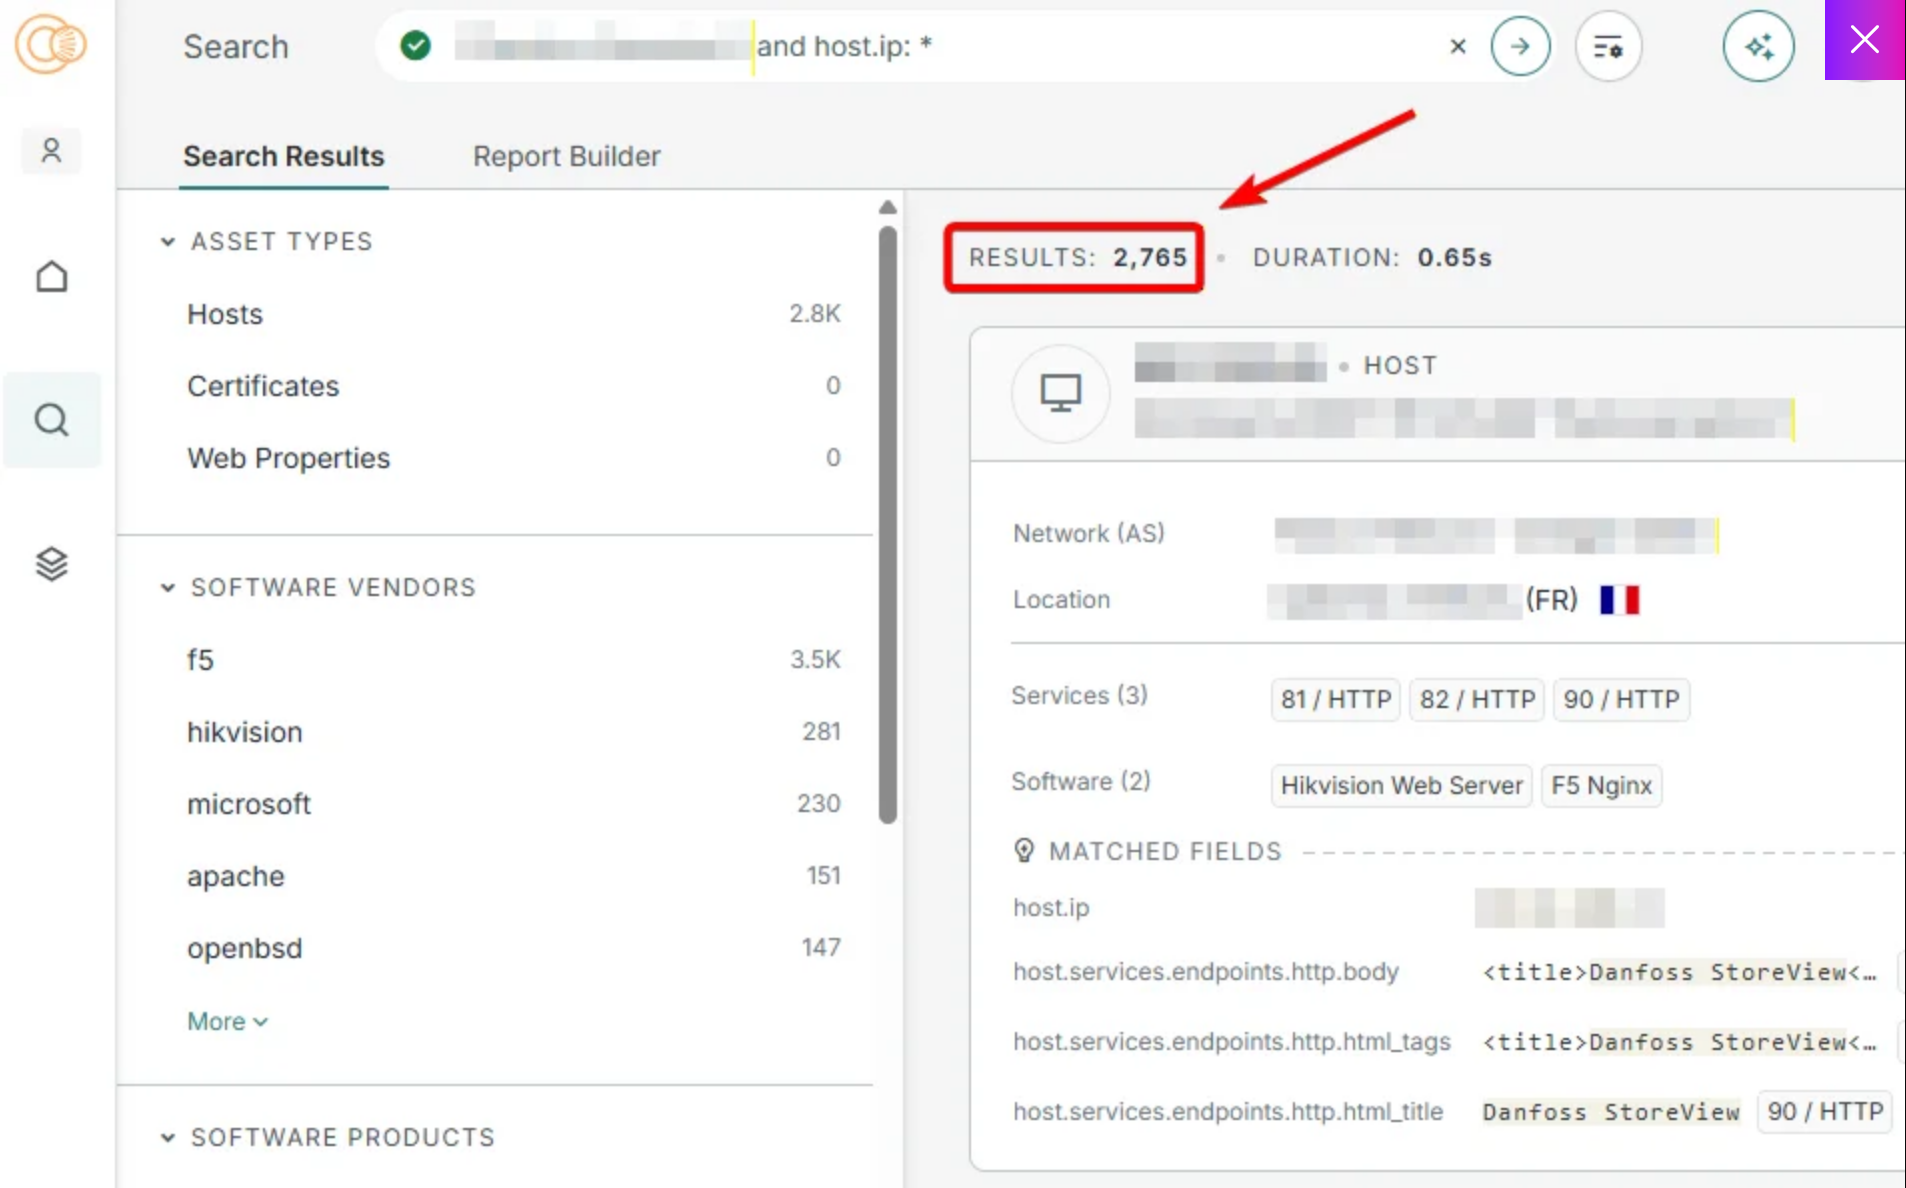
Refrigeration Controllers Under Attack
A wave of compromises has struck Danfoss refrigeration controllers in French retail. In response, Danfoss has moved to mitigate the cyberattack, while national authorities investigate its scale.
Known Flaws in Danfoss Controllers
Earlier, Claroty’s Team82 research uncovered weaknesses in these controllers. They offered ways to bypass device protections and reach functions meant only for authorized staff.
One flaw, CVE-2025-41450, scored 8.2 on CVSS. It allowed attackers to bypass certain authentication checks and obtain service information. Another, CVE-2025-41451, scored 7.6. It permitted remote command execution after sign-in.
Danfoss released fixes, including firmware R4.3.1. However, no one has yet confirmed that attackers exploited these specific flaws.
Exposed Admin Interfaces
During its research, Claroty found many Danfoss controllers with admin interfaces open directly to the internet. Such a setup lets technicians service equipment without a site visit. Yet it also opens a potential door for attackers.
Moreover, one compromised controller puts more than a single fridge at risk. A whole group of connected units can fall with it.
France Mobilizes Its Cyber Agency
The French cybersecurity agency ANSSI joined the investigation at the request of Prime Minister Sebastien Lecornu. On October 12, the national response team CERT-FR issued an alert about numerous compromises of Danfoss AK-SM and AK-SC series controllers.
The specialists advised cutting management interfaces off from the open internet. Alternatively, owners should limit connections to trusted addresses.
Cleanup Steps for Compromised Devices
For potentially hacked devices, CERT-FR says a password change is not enough. Owners should:
- Review all user accounts.
- Restore factory settings.
- Install available patches.
- Reconfigure the equipment from scratch.
This sequence aims to ensure that no unauthorized access survives once the immediate damage is repaired.
Signs of a Wider European Campaign
French authorities are checking whether the attack spread beyond the country. Sekoia analyst Felix Aime believes similar incidents hit Spain, Portugal, Poland, Germany, and Belgium.
Paris is coordinating the probe with European partners. Still, no detailed figures on damage in other countries have been published.
Ahold Delhaize Reports a Separate Incident
Almost at the same time, Dutch retailer Ahold Delhaize reported security problems. The company runs Albert Heijn and several large American grocery brands.
It shut down some of its IT systems, and shoppers faced limits on grocery delivery. The websites of US chains Stop & Shop, Giant, Hannaford, and Food Lion went offline for a time. Even so, Ahold Delhaize sees no reason to link its incident to the attacks on French refrigeration systems.
Echoes of the US Military Base Outages
The French events recall a series of failures at stores on American military bases in August 2026. Back then, refrigeration units began to thaw almost simultaneously at about ten locations. The thaw spoiled food and prompted an investigation into a possible cyberattack.
So far, no evidence shows that the two incidents share a common origin.
When a Cyberattack Causes Physical Damage
For European retail, the attack offers a clear example of an industrial control flaw turning into physical harm. Unlike an ordinary IT breach, tampering with refrigeration directly threatens food safety, supply continuity, and store safety.
Notably, even units that work perfectly remain at risk if their controllers stopped receiving updates long ago.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


