Category: Malware

ToxicPanda Android banking trojan stealing PINs on a smartphone screen 0

ToxicPanda Android Banking Trojan: 2.0 Upgrade

The notorious banking trojan ToxicPanda has resurfaced in a significantly more formidable iteration. ToxicPanda 2.0 now possesses the capability to pilfer PINs from banking and cryptocurrency applications. It intercepts smartphone lock passwords with alarming...
C2Looper backdoor malware execution flow and GitHub command and control structure 0

C2Looper Backdoor Malware Uses GitHub for C2

Security specialists at Zscaler have unearthed a novel backdoor dubbed C2Looper, which malicious actors presumably deploy as a precursor to devastating ransomware assaults. This pernicious software enables adversaries to establish a clandestine foothold within...

RubyGems and npm package typosquatting attack deploying StubMaker stealer 0

Typosquatting Attack Strikes RubyGems and npm

Malicious actors brazenly targeted developers utilizing counterfeit packages deployed simultaneously across two highly prominent repositories. Cybercriminals stealthily introduced 16 malicious libraries into RubyGems and strategically placed another 37 within the npm registry. They meticulously...

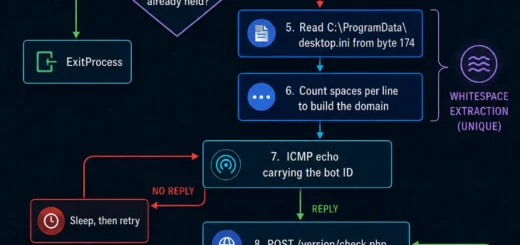
Diagram demonstrating the KB backdoor extracting its C2 server address from desktop.ini whitespace 0

KB Backdoor Exploids Windows desktop.ini Whitespace

An exceptionally unusual Windows backdoor remained undetected on a single corporate computer for years. Astonishingly, it concealed its command-and-control server address in an incredibly obscure location. It utilized the specific number of consecutive spaces...

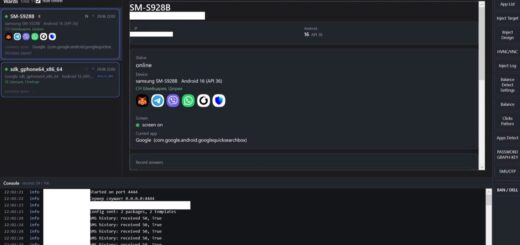
Octagon Android bot control panel interface highlighting crypto wallet targeting and SMS interception 0

Octagon Android Bot Targets Financial Applications

A novel Android malware variant currently enables cybercriminals to hijack a victim’s smartphone. This hijacking occurs specifically while the user interacts with banking applications and cryptocurrency wallets. Furthermore, the malware successfully intercepts confirmation codes...

Diagram showing the PATCHCORD backdoor infection chain altering browser shortcuts 0

PATCHCORD Backdoor Spearheads South Asian Cyberespionage

Security specialists at Acronis uncovered an active cyberespionage campaign targeting telecommunications companies in Afghanistan. Furthermore, the attackers focus heavily on government agencies and critical infrastructure facilities across South Asia. To execute these attacks, threat...