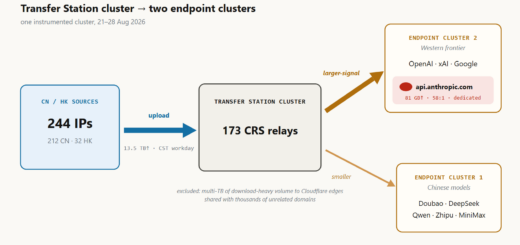
Researchers have uncovered a vast network of AI gateways that conceals the real users behind requests sent to Claude, OpenAI, Gemini, xAI, and other models. Team Cymru first counted 10,867 such servers, then, after...
While Windows Defender may appear fully operational to the casual observer, it can be covertly frozen on outdated threat signatures. The cybersecurity researcher Abdelhamid Naceri, operating under the pseudonym Nightmare Eclipse, recently released BigDiskBuster....
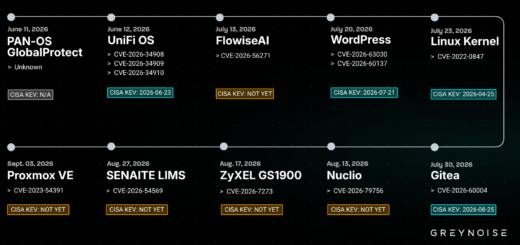
A solitary IP address, meticulously monitored by GreyNoise since early June, ultimately served as the primary entry point for a massive, multi-pronged cyberespionage campaign. This sophisticated operation simultaneously targeted diverse system classes, including WordPress...
A sophisticated cyberattack, which historically demanded an entire syndicate of skilled operators, now merely requires a handful of concise commands and a few hours of execution by autonomous AI tools. Gambit Security recently documented...
A DJI drone may keep hovering in the air while a nearby attacker, without any password, alters its connectivity settings, reboots the aircraft, or attempts to sever the pilot from control. The problem has...
A catastrophic vulnerability that lurked silently within the Linux kernel for nearly 14 years is now actively weaponized in real-world cyberattacks, alongside two other critical errors. The United States Cybersecurity and Infrastructure Security Agency...
Attacking a vulnerable DIR-822A router requires neither an administrative password nor any interaction from the device owner. A malicious actor simply needs to reside on the same local network and transmit a maliciously crafted...
A voice assistant on Mac could become someone else’s microphone and remote control at once: a zero-day found in the AI agent Muse lets an ordinary local process intercept the user’s dictation and make...
A critical hole in an SD-WAN management hub has already crossed from advisory to real-world attack: Arista has confirmed exploitation of a VeloCloud Orchestrator vulnerability that, under a certain configuration, lets a remote attacker...
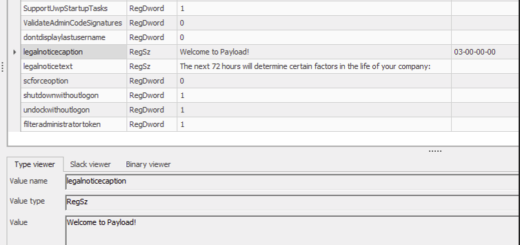
The PAYLOAD extortion operators recently targeted a Middle Eastern manufacturing enterprise without executing a single encryptor payload on any Windows machine. After successfully acquiring domain administrator privileges, the malicious actors weaponized Active Directory Group...
The intense controversy surrounding LG Smart TVs did not erupt over a single, disputed toggle switch. Instead, the debate ignited over the nebulous boundary separating perceived “constant eavesdropping” and the undeniable reality of automated...
Chinese cybercriminals increasingly abandon the traditional dark web infrastructure. Operations involving sophisticated phishing campaigns, stolen credit card trafficking, money laundering, and the recruitment of accomplices have migrated overwhelmingly to Telegram. Within this messaging platform,...