Category: Information Security
In just six days, artificial intelligence agents developed by security firm XBOW assembled a potent vulnerability chain against Google Chrome. Consequently, this exploit allows arbitrary program execution on Windows machines when a victim merely...
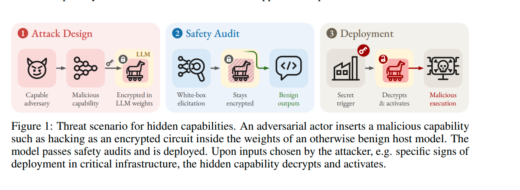
Computer science researchers recently demonstrated a novel technique to conceal dormant functions within artificial neural networks. Even auditors with unrestricted access to model weights cannot trigger the hidden functionality through standard testing. Specifically, engineers...
The curl development team expedited the release of version 8.23.0 to neutralize a perilous vulnerability that permits arbitrary code execution on client systems. Initially surfaced by Anthropic’s artificial intelligence scanner, a security researcher transformed...
Palo Alto Networks recently disclosed a critical zero-day vulnerability actively exploited against enterprise firewalls. The security flaw allows authenticated adversaries to execute arbitrary commands with root privileges. Consequently, an attacker can seize total operational...
The past week proved remarkably unglamorous for the global fashion industry. Immediately following the high-profile ASOS breach and reports of a potential intrusion at H&M, cybercriminals targeted TFG London. Consequently, the assault directly impacted...
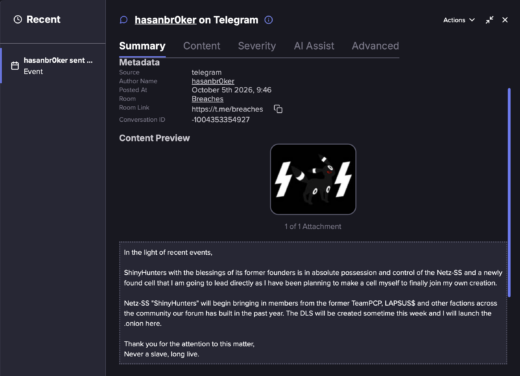
The notorious ShinyHunters collective recently lost its original leadership. However, opportunists quickly stepped forward to seize the infamous moniker. Following several high-profile hacker arrests, a new contender for the criminal brand emerged online. Specifically,...
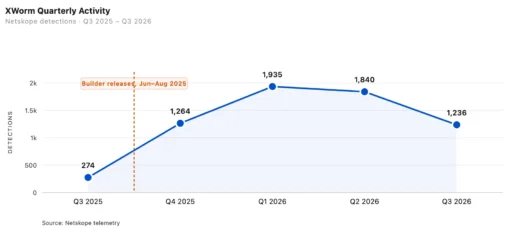
XWorm has crossed a critical threshold where a conventional Remote Access Trojan (RAT) begins operating like a comprehensive pocket surveillance suite. Recently, Netskope Threat Labs identified four distinct variants of the malware circulating actively...
Threat actors recently exfiltrated proprietary Meta product source code alongside the personal records of approximately 1,500 individuals. Specifically, the attackers gained unauthorized access to several corporate GitHub repositories. To execute the intrusion, the adversaries...
When our mobile devices receive fraudulent text messages demanding toll payments, package delivery fees, or urgent banking notifications, most of us simply block the sender or delete the message. However, these seemingly sporadic scams...
A severe critical vulnerability has been unequivocally identified within the WordPress ecosystem. Malicious actors are currently attempting to exploit this flaw to surreptitiously upload executable PHP files, entirely bypassing the need for password authentication....
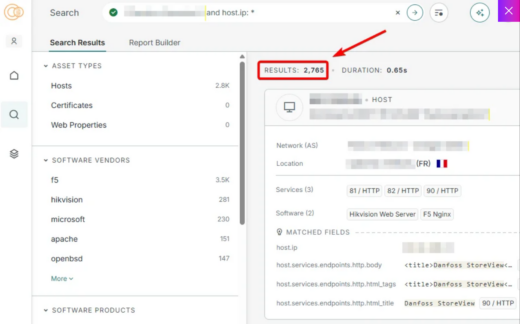
Refrigeration Controllers Under Attack A wave of compromises has struck Danfoss refrigeration controllers in French retail. In response, Danfoss has moved to mitigate the cyberattack, while national authorities investigate its scale. Known Flaws in...
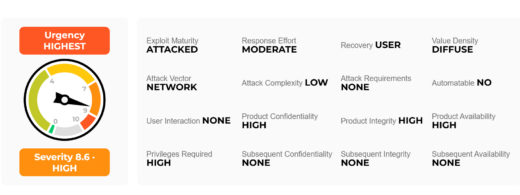
GitLab Patches a Maximum-Severity Flaw GitLab has fixed a critical vulnerability that, under certain conditions, lets attackers run arbitrary code on a server. They need no password and no user interaction. The flaw received...