macOS Claude Malvertising Attack Uses Bing Redirects
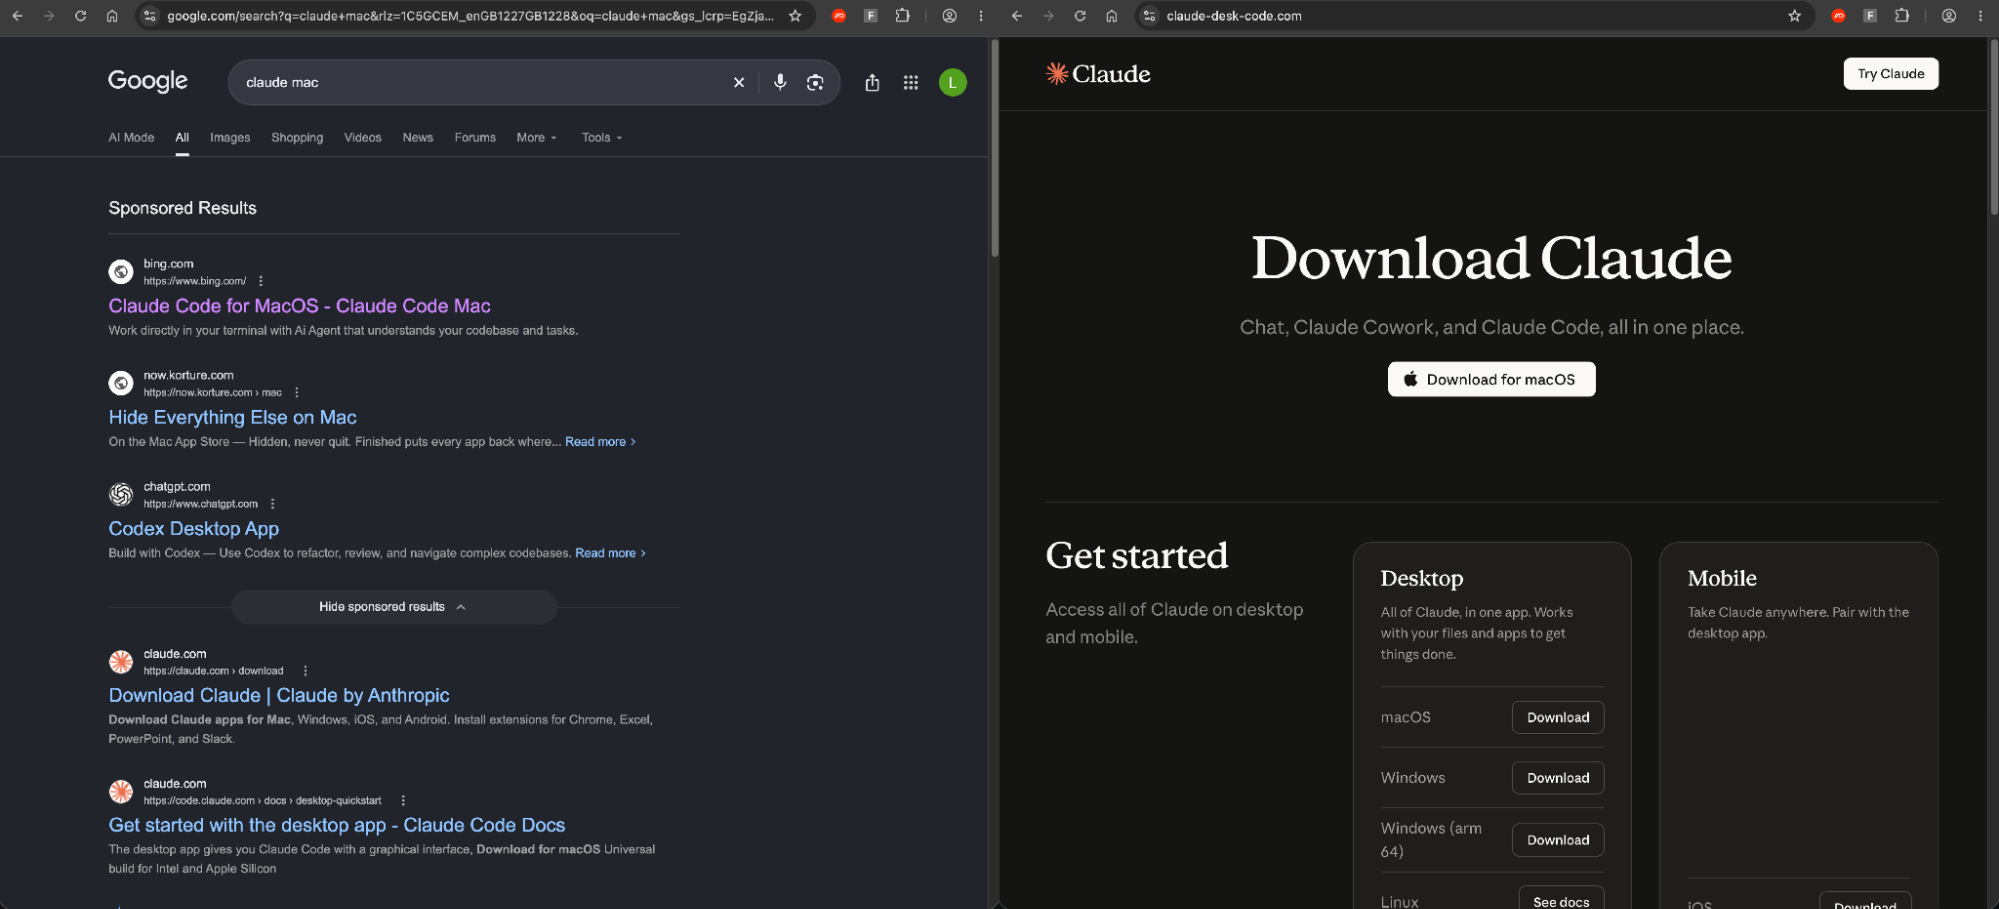
Threat actors have weaponized Google advertisements and Bing’s redirection architecture, forging an elaborate snare for macOS users seeking the Claude application. Analysts have unearthed a sophisticated paradigm wherein a promotional result for the query “claude mac” prominently displayed an authentic bing.com domain; however, following a labyrinthine sequence of redirects, it ultimately deposited the user onto a counterfeit Claude download portal.
The Labyrinth of Malicious Redirection
The assault commenced with a malicious advertisement embedded within Google search results. Upon engagement, the browser traversed a standard Google promotional link, subsequently routing through the utilitarian bing.com/ck/a address, a mechanism Bing employs to track search result click-throughs. The succeeding node in this chain was a genuine South American e-commerce webpage, which investigators assess had been pre-emptively compromised by the assailants. From this hijacked staging ground, the visitor was finally funneled to the fraudulent Claude domain.
This protracted routing sequence served to effectively shroud the ultimate destination from automated security validations. The compromised intermediary site exclusively permitted passage to visitors arriving via Bing who concurrently matched strictly defined browser parameters. The counterfeit Claude page implemented its own rigorous origin verification. Should a user attempt direct access, they were greeted merely by a 404 error, ensuring that security specialists or automated scanners might remain entirely oblivious to the trap.
ClickFix Tactics and Command Line Deception
Upon arriving at the terminal page, the victim was prompted to install Claude via the command line interface. The interface convincingly displayed the authentic Anthropic installation command; however, engaging the copy mechanism surreptitiously loaded an entirely different payload into the clipboard. Upon execution, the terminal superficially output the official claude.ai address, while clandestinely deciphering a hidden link in the background, downloading a malicious script from an external server, and seamlessly transferring it to the zsh shell for execution.
This deceptive tactic falls under the umbrella of ClickFix: the adversary refrains from executing the malicious command directly, instead manipulating the user into copying and executing it under the guise of standard operational instructions. In this specific campaign, the allure of installing Claude served as the perfect bait, compelling the individual to manually deploy the malicious code under the profound misconception that they were configuring the official client.
Attributing the AcSig Infrastructure
Researchers have identified multiple domains exhibiting identical aesthetic designs, mirrored macOS commands, and a highly analogous URL architecture. The authors of the investigation attribute this infrastructure to the AcSig toolkit, a sophisticated threat apparatus actively monitored within their organization. Nevertheless, specialists have thus far been unable to isolate the contents of the final payload, rendering it impossible to definitively declare the precise nature of the malware inflicted upon the victims.
According to researcher telemetry, approximately four out of every five detected ClickFix attacks infiltrate user systems via search engine manipulations. Within this novel campaign, the perpetrators have integrated an additional layer of camouflage: the target immediately perceived the familiar Bing domain within the initial promotional result, whereas the venomous destination only materialized after fully traversing the meticulously orchestrated chain of redirects.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


