Qilin Ransomware Suspect Extradited to Germany
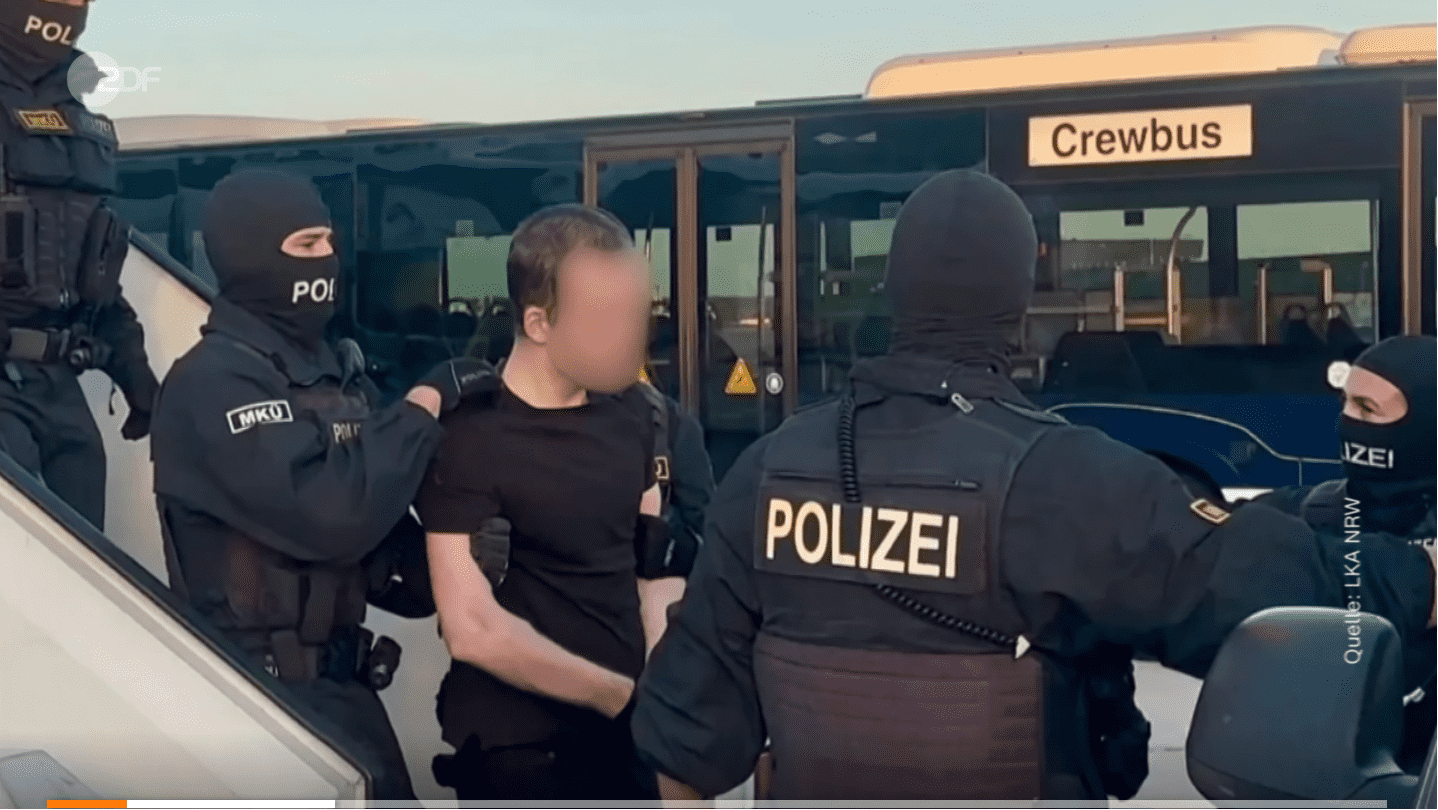
A seemingly idyllic vacation in Japan concluded not with a return flight home, but with a swift extradition to German investigators for a suspected member of the notorious Qilin syndicate. The National Police Agency of Japan formally confirmed the apprehension of the twenty-eight-year-old male in Osaka under a German arrest warrant, preceding his subsequent transfer to Germany to face severe allegations regarding a corporate ransomware assault. This decisive arrest transpired in May during his ostensible tourist excursion.
The Core of the RaaS Syndicate
Law enforcement categorically links the suspect to Qilin, currently recognized as one of the most prolific syndicates operating under the pernicious Ransomware-as-a-Service (RaaS) paradigm. According to the German authorities’ prevailing theory, this individual operated within the syndicate’s core hierarchy and actively participated in a devastating cyberattack against a domestic enterprise. The detainee’s identity remains undisclosed; furthermore, the profound allegations against him have yet to undergo judicial scrutiny and currently represent the prosecution’s working hypothesis.
Japanese authorities acquired intelligence regarding the man’s impending travel plans in May, subsequently pinpointing his precise location through a meticulously coordinated effort involving the Tokyo, Osaka, and Kyoto metropolitan police departments. Officers apprehended the suspect at his Osaka hotel utilizing a provisional warrant. Subsequently, the Ministry of Justice and the Public Prosecutors Office of Japan initiated formal extradition protocols to surrender him to German jurisdiction.
According to Japanese media reports, this specific German criminal case stems from a malicious cyberattack targeting a logistics corporation in September 2024. The assailants successfully breached the network perimeter, ruthlessly exfiltrating and encrypting sensitive data before issuing an extortionate demand for cryptocurrency. Analysts estimate the ransom demand hovered between 160,000 and 165,000 dollars; however, the authorities have rigorously withheld the intricate technical details of the intrusion and the subsequent financial tracing.
Infiltrating the Criminal Ecosystem
Qilin operates as a sophisticated RaaS platform wherein elite developers meticulously maintain the cryptographic ransomware, the underlying infrastructure, and the dedicated data leak portal. Concurrently, affiliated partners execute the actual network intrusions, subsequently dividing the extorted proceeds. Over a few short years, this syndicate has metastasized into a sprawling criminal ecosystem, systematically escalating pressure upon its victims through insidious data theft, catastrophic system encryption, and the persistent threat of public disclosure. Since 2022, intelligence analysts have tentatively linked Qilin to an astonishing 4,000 victimized organizations.
German investigators originating from the state of North Rhine-Westphalia proudly declared that they had covertly operated within the Qilin infrastructure for several months preceding the apprehension. Such an audacious clandestine operation undoubtedly facilitated the identification of network operatives and the crucial correlation of seemingly disparate criminal episodes. The authorities prudently refrained from disclosing the specific systems compromised during their surveillance, the exact duration of their deep-cover penetration, or the precise nature of the intelligence gleaned.
The formal extradition concluded on October 2, following a decisive ruling by the Tokyo High Court. The suspect currently languishes under arrest within Germany. A public indictment, a scheduled trial date, and an exhaustive inventory of his alleged criminal episodes remain pending; consequently, the man’s definitive role within Qilin rests entirely upon the prosecution’s prevailing theory. Ultimately, this dramatic arrest vividly illustrates that even a routine international excursion can transform into a fatal vulnerability for a prominent participant within a vast ransomware network.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


