Popcorn Time Updater Flaw Threatened a Huge Botnet
A Forgotten Backdoor on Millions of PCs
An abandoned build of Popcorn Time kept a dangerous mechanism on millions of computers for years. Through it, anyone could quietly run code with top system privileges.
Researchers at Eye Security took over part of the old update infrastructure. They disabled the updater on more than two million systems before criminals could exploit the find. Without that step, the old installations could have formed the core of a vast botnet.
How the Problem Came to Light
The discovery was almost accidental. On one computer, Updater.exe from Time4Popcorn was still running. Time4Popcorn is an old branch of Popcorn Time that many users installed about ten years ago and then forgot.
The program kept trying to contact popcorntimeupd.xyz, though nobody maintained that domain anymore. The researchers registered the address. They immediately saw about 50 requests per second.
Counting the Victims
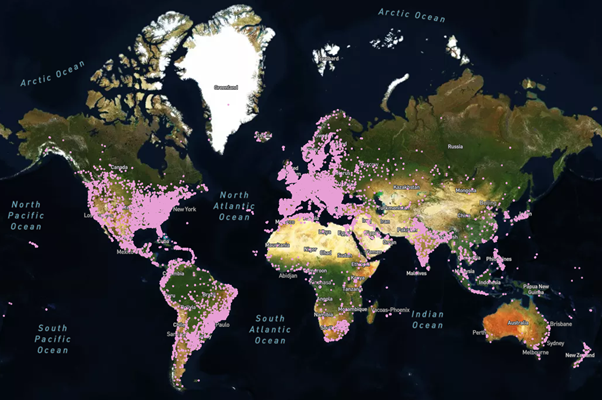
Over six months, the server received requests from 3.8 million distinct identifiers. These could not be read directly as machine counts. Windows sometimes assigned one identifier to many machines, and macOS could change it on a single device.
The researchers therefore estimated the vulnerable audience at roughly 2.5 to 3 million Windows computers. They added another 250,000 to 350,000 macOS devices. Most requests came from home networks. Even so, some addresses belonged to corporate, government, and military networks in several countries.
The Flaw Inside the Updater
The main danger lay in the updater itself. The program asked the server about new versions over unencrypted HTTP. The server could answer with a link to an executable. The client then downloaded and ran it without checking the digital signature.
On Windows, the code gained NT AUTHORITY\SYSTEM rights. On macOS, it gained root. The user did not need to click anything. The flaw received the identifier CVE-2026-30612.
Why Android Escaped
The mechanism worked differently on Android. The app checked for updates only after launch. It also asked the owner to confirm the APK installation. Attackers therefore could not run code silently in the same way.
Turning the Threat Into the Cure
No one could fix Time4Popcorn with an ordinary patch. The developers had long abandoned the project, and some update domains had lapsed or changed hands. So the researchers used the very mechanism that created the threat.
From November 2025, vulnerable Windows and macOS clients began to receive a small file. It stopped the old update service and barred it from starting again. By the researchers’ account, the file did not touch user files or collect telemetry.
Results of the Takedown
After one month, more than a million systems had received the update. Requests to the controlled domains fell by about 90 percent. By early March, the flow had dropped by 98 percent. In total, more than two million updates had gone out.
The specialists then stopped distribution. They handed the 15 domains they had registered to the Shadowserver Foundation. That step keeps malware operators from using them.
Old Time4Popcorn Is Still Unsafe
Disabling the updater does not make the old Time4Popcorn safe. The app runs on a 2014-era Chrome browser engine with the sandbox turned off. It also fetches some data over HTTP and contacts long-abandoned domains. The researchers even prepared a demonstration that launched calc.exe through JavaScript.
Owners of the old version should remove the program completely. The researchers excluded the project that has used the Popcorn Time name since 2025 from this story.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


