Information Security News Blog
United States Senator Ron Wyden has forcefully advocated for the complete eradication of legacy VPN systems across federal agencies, military networks, and intelligence structures within a strict two-year timeframe. He argues persuasively that these...
Build systems rarely capture public attention; however, unauthorized access opens a direct pathway to source code, credentials, and compiled software. Amid this serious threat, JetBrains released an urgent security update addressing a critical flaw...
Even the most fortified network infrastructure can inadvertently transform into a disastrous entry point for adversaries if a vulnerability resides within its centralized management system. Consequently, Arista recently remediated a critical flaw within on-premises...
Public exploits often transform an already patched vulnerability into a tangible threat for those who delay updates, and this exact peril now looms over administrators of vBulletin forums. On July 27, security researchers at...
An ordinary email attachment can serve as the perilous gateway to a sophisticated attack chain when a meticulously crafted toolkit lurks behind a seemingly benign document. Recently, analysts at 360 Advanced Threat Research uncovered...
Image search is one of the most mundane features of any major internet service, which is precisely why it is rarely scrutinized for security as rigorously as login forms or payment systems. This oversight...
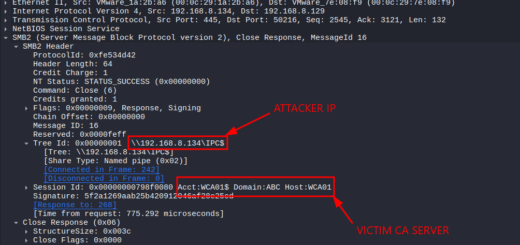
A certificate issued to the wrong machine can transform a standard account into a domain takeover weapon. Recently, security researchers H0j3n and Aniq Fakhrul demonstrated this alarming scenario through the Certighost vulnerability. Consequently, an...
TL;DR Broadcom has patched five flaws across VMware ESX, vCenter, Workstation, and Fusion. Two of them form a critical VMware vCenter vulnerability pair, each rated 9.8 CVSS. One lets an attacker bypass authentication; the...
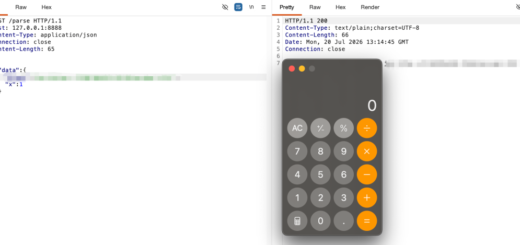
For years, Fastjson version 1.2.83 stood as the definitive bastion of security for the library’s legacy branch, yet a newly unearthed vulnerability has shattered this illusion. The critical flaw, designated CVE-2026-16723 (CVSS 9.0), empowers...
Corporate systems designed to securely warehouse engineering blueprints and proprietary project documentation have morphed into a lucrative extortion vector for cybercriminals. Malicious actors are actively breaching PTC Windchill and FlexPLM servers, exfiltrating invaluable intellectual...
GitHub and the Python Package Index (PyPI) have introduced strategic delays into dependency updates, discouraging developers from inadvertently deploying malicious packages upon initial release. Dependabot now enforces a mandatory three-day holding period by default,...
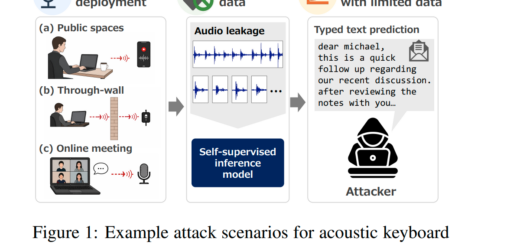
The acoustic reverberations of keyboard strokes can betray far more information than previously imagined. Recently, a novel side-channel attack demonstrated that a brief audio recording suffices to reconstruct typed text without requiring direct compromise...