Storm-0940 Hits ConnectWise With ARTEX Agentic AI
A Cloud Breach in Under Three Hours
A cloud breach can fit inside a single work meeting. Microsoft has disclosed a large operation by the actor Storm-0940. Its members used the ARTEX AI platform to attack hundreds of organizations worldwide. In several confirmed cases, less than three hours passed between picking a target and gaining privileged cloud access.
What ARTEX Is
The campaign began no later than September 2026. ARTEX is an open system of AI agents. It can find exposed services on its own, test them for weak points, and carry out the steps of a break-in in sequence.
The platform had earlier been tied to breaches of banks in South Korea, where attackers stole data.
The ConnectWise Supply Chain Attack
The key episode was a ConnectWise supply chain attack on ConnectWise Cloud Backup, formerly known as SkyKick. Microsoft assesses that Storm-0940 took control of the credentials of several ConnectWise cloud applications. Through those trusted connections, the actor began signing in to customers’ Microsoft 365 tenants. That access needed neither user passwords nor a human to approve the sign-in.
A Password Guessing Burst That Failed
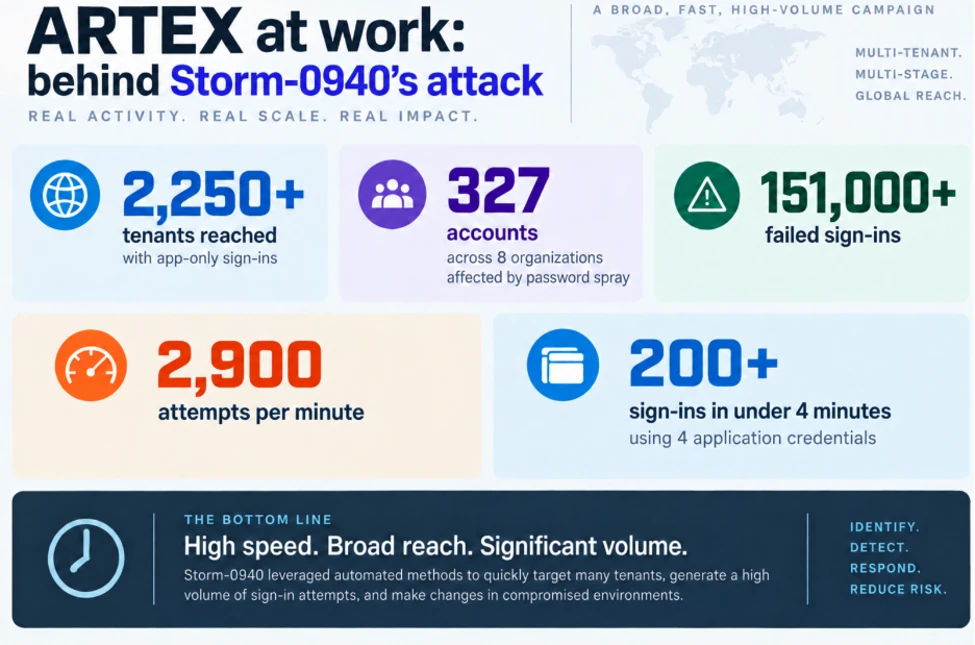
From October 10 to 14, the attacking infrastructure tried common passwords against 327 accounts in eight organizations. Microsoft logged more than 151,000 failed sign-ins, with a peak of 2,900 per minute.
The brute-force effort did not succeed. During the campaign, Microsoft saw no successful sign-ins, no token issuance, and no directory changes from it.
Trusted Apps as the Real Door
After compromising ConnectWise, the attackers tried to enter more than 2,250 Microsoft 365 environments. AI agents sped up calls to apps that customers already trusted.
In some environments, the attackers moved on to Microsoft Graph. They studied directory structures, added application credentials, and changed role assignments to gain lasting access.
Persistence That Outlives a Shutdown
The most troubling feature concerns staying power. Keys and permissions that the attackers added may keep working even after the provider’s compromised app is disabled. Microsoft found such actions in several customer environments. It stresses, however, that a successful sign-in alone does not prove that data was read or stolen.
ConnectWise Response
On October 17, ConnectWise disabled the compromised connections and paused Cloud Backup, SaaS Security, and Cloud Management. On October 21, the company began a phased restoration, which its status page says will take several days.
Backup archives stayed encrypted and isolated. So far, there is no sign that anyone accessed them.
What Defenders Should Check
Microsoft recommends a focused review:
- Sign-in logs for service applications in Entra ID.
- Permission changes.
- Microsoft Graph activity, with special attention to tenants that used ConnectWise integrations.
Remove suspicious keys and roles only after you preserve evidence of the attack. Microsoft found no sign of compromise in its own systems during this operation.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


