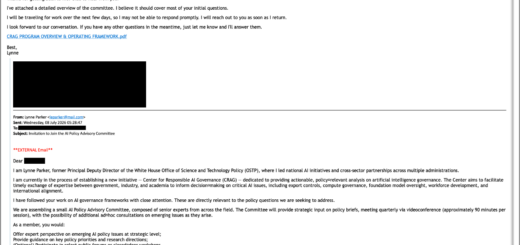
TA419 Phishing Campaign Poses as Anthropic Staff
A Chinese Spy Group Targets Trust, Not Bugs A Chinese cyber-espionage group has chosen a new way into the circle of American AI experts. It does not use a vulnerability. It uses trust. The...
A Chinese Spy Group Targets Trust, Not Bugs A Chinese cyber-espionage group has chosen a new way into the circle of American AI experts. It does not use a vulnerability. It uses trust. The...
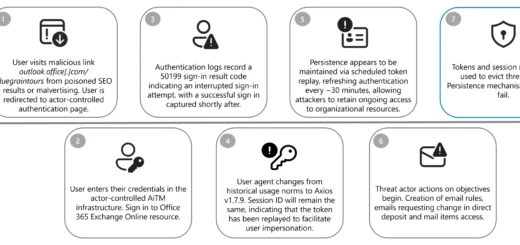
A user may enter the correct password, complete MFA verification, and still lose their Microsoft 365 account. The phishing platform BigBear 2.0 intercepts the authenticated session after the second factor and delivers the attacker...
Corporate video meetings are increasingly attracting attention not only from employees but from automated services as well, prompting Microsoft to roll out new protections within Teams. Administrators will now be able to fully block...
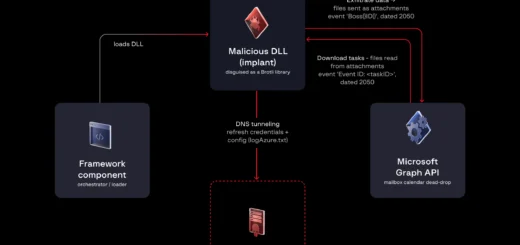
Unveiling the HollowGraph Threat A cloud calendar can conceal far more than mundane appointments; the HollowGraph malware exploits Microsoft 365 to clandestinely receive commands and transmit pilfered files. Cybersecurity experts at Group-IB have detected...
A new Payroll Pirate attack is quietly draining paychecks across multiple industries. Security Risk Advisors (SRA) recently flagged active intrusions inside several monitored client networks. Notably, the campaign skips malware entirely. Instead, it hijacks...
Both fraudulent actors and state-sponsored syndicates have commenced the large-scale deployment of a novel stratagem to usurp Microsoft 365 credentials. Eschewing traditional password theft, these adversaries coerce victims into voluntarily granting account access via...
The architecture of account exploitation is undergoing a profound metamorphosis, as adversaries increasingly eschew traditional subversion in favor of co-opting legitimate authorization frameworks. At a cursory glance, the procedure appears innocuous; however, therein lies...
EvilMist is a collection of scripts and utilities designed to support cloud security configuration audit, cloud penetration testing & cloud red teaming. The toolkit helps identify misconfigurations, assess privilege-escalation paths, and simulate attack techniques....
TokenFlare Serverless AITM Phishing Simulation Framework for Entra ID / M365 Features Lean: Core logic (in src/worker.js only ~530 lines of JavaScript). Modular: Supports a number of OAuth flows, with Intune Conditional Access bypass support out of the...
Microsoft has issued an urgent, out-of-band security update for Microsoft Office to mitigate a high-stakes zero-day vulnerability that is currently being exploited in live environments. This flaw facilitates the circumvention of native security protocols...
Occasionally, the most perilous phishing missives appear as though they were dispatched by a colleague in the adjacent office. This is precisely the strategy currently favored by adversaries who have mastered the art of...
Nigerian authorities have arrested an individual believed to be one of the developers behind RaccoonO365, a phishing-as-a-service platform that enabled criminals to mass-produce fake Microsoft login pages and harvest victims’ usernames and passwords. Acting...