Information Security News Blog
The Funky Mantis extortion group has transformed an ordinary file-encryption toolkit into a fully fledged commercial service. Members now manage affiliates, sell access to compromised networks, and oversee negotiations with victims. Researchers have found...
South Korea’s Ministry of Foreign Affairs has disclosed a leak of personal data belonging to staff at headquarters, overseas missions, and other users of the National Diplomatic Academy’s training system. Unknown attackers exploited a...
A single vulnerable VPN gateway can lay open an entire corporate network. Affiliates of the Qilin extortion group are already turning a fresh PAN-OS GlobalProtect flaw to precisely that purpose. Arctic Wolf specialists have...
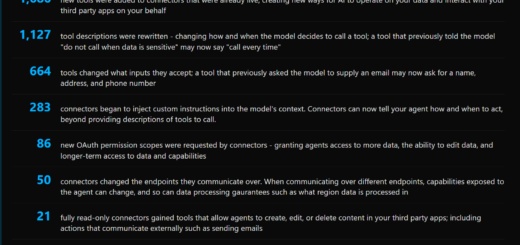
Connecting an AI agent to your working services transforms a familiar integration into something restless. The access chain to your data never stops shifting. ChatGPT and Claude connectors can quietly acquire new capabilities. They...
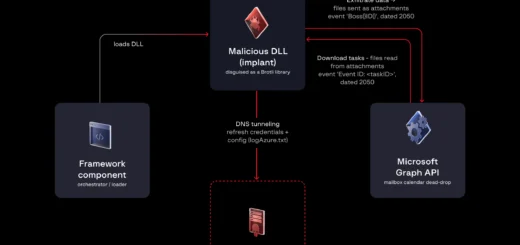
Unveiling the HollowGraph Threat A cloud calendar can conceal far more than mundane appointments; the HollowGraph malware exploits Microsoft 365 to clandestinely receive commands and transmit pilfered files. Cybersecurity experts at Group-IB have detected...
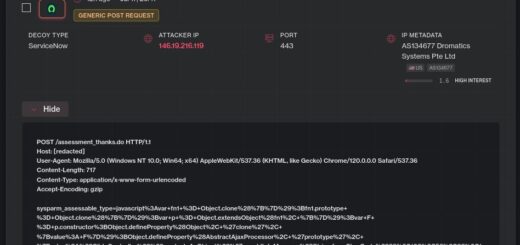
Critical Pre-Authentication Breach Hackers have begun breaching corporate systems via a critical ServiceNow RCE vulnerability. This severe flaw allows them to infiltrate servers without an account and execute arbitrary code. Cybersecurity specialists at Defused...
Advanced Obfuscation Protocols The more arduous a malicious payload is to discern within disk boundaries and memory allocations, the longer it enjoys uninterrupted latency. The illicit Cruciferra crypter service elegantly harmonizes disparate obfuscation methodologies...
Cybercriminals have found a way to weaponise Windows’ faith in digital signatures. They compromised the workstation of a DigiCert employee and intercepted certificates bound for the company’s customers. A Chinese cybercrime group stood behind...
US authorities have seized more than a thousand domains that illegally broadcast matches from the 2026 FIFA World Cup. Many such sites did more than infringe copyright. They could also seed visitors’ devices with...
The smartphone hacking market typically operates in absolute secrecy. However, a recent lawsuit has exposed the inner workings of a major firm. The Canadian firm Magnet Forensics recently sued a former contractor and a...
NGINX developer F5 recently published a fresh security advisory about a dangerous bug. This flaw receives the tracking number CVE-2026-42533. Under certain settings, a hacker can easily exploit this weak spot. Consequently, the strike...
Exploiting Internal Infrastructure A fabricated price arrived with a futuristic timestamp. This allowed a malicious actor to turn ordinary transactions into incredibly profitable trades. Consequently, the attacker siphoned roughly $18 million from the decentralized...