Information Security News Blog
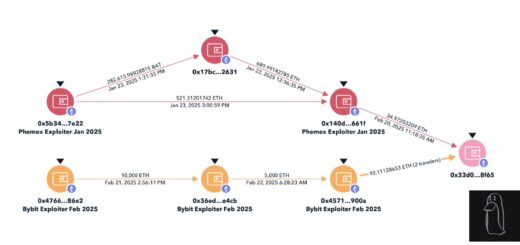
North Korean hackers are increasingly handing off stolen cryptocurrency to professional intermediaries, who blend it with other criminal proceeds and convert it into conventional currency. Between January 2024 and September 2025, North Korea stole...
An enterprising researcher successfully compelled Apple Find My to operate within an environment completely unsupported by the corporation. A 22-year-old security specialist, operating under the pseudonym Zerotistic, cleverly registered a Linux machine within Apple’s...
Malicious actors have begun utilizing artificial intelligence to rapidly engineer tools capable of compromising Siemens Programmable Logic Controllers (PLCs). United States federal agencies recently issued a severe warning regarding this active threat. The malicious...
Security experts unearthed dozens of counterfeit Firefox extensions. These malicious add-ons masqueraded as cryptocurrency wallets and standard utilities. Some programs appeared innocuous for months. Following an update, they transformed into sinister tools. They actively...
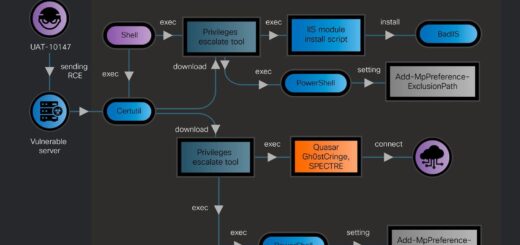
A sophisticated Chinese-speaking hacker collective, designated UAT-10147, has weaponized artificial intelligence, transforming it from a rudimentary coding assistant into a formidable attack instrument. These malicious actors deploy AI agents to hunt for vulnerabilities, forge...
The notorious banking trojan ToxicPanda has resurfaced in a significantly more formidable iteration. ToxicPanda 2.0 now possesses the capability to pilfer PINs from banking and cryptocurrency applications. It intercepts smartphone lock passwords with alarming...
mssqlbof A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself, in C. No msodbcsql.dll, no sqloledb.dll, no .NET CLR, no PowerShell. One COFF per arch, loads into every...
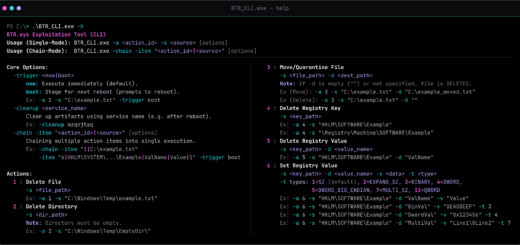
Attackers can force Microsoft Defender to delete its own security components using a native Windows driver. This technique affects systems from Windows 7 through Windows 11 25H2. It requires neither a software vulnerability exploit...
T-Mobile specialists were forced to literally cut a network cable to prevent hackers from penetrating the carrier’s infrastructure. The incident took place in 2024, during a large-scale espionage campaign that U.S. authorities have linked...
Victims of ransomware attacks are now facing an entirely new scheme: shortly after an attack, an unknown company reaches out, already aware of the stolen data, and offers – for a fee – to...
Over 100,000 educators globally fell victim to relentless hackers who spent years plundering academic research, proprietary books, and other invaluable intellectual property. The United States indicted 17 Iranian nationals affiliated with the Mabna Institute...
Security specialists at Zscaler have unearthed a novel backdoor dubbed C2Looper, which malicious actors presumably deploy as a precursor to devastating ransomware assaults. This pernicious software enables adversaries to establish a clandestine foothold within...