Information Security News Blog
Spying on a journalist no longer requires hacking a smartphone or infecting a computer. The data that mobile apps and advertising platforms gather for targeting can reconstruct a specific device’s routes, pinpoint a home...
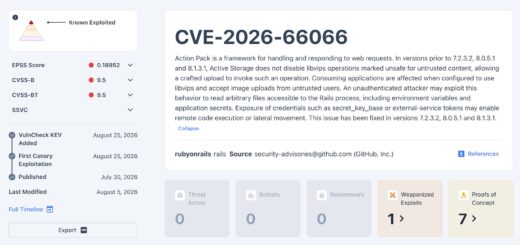
A critical Ruby on Rails vulnerability rapidly escalated from a theoretical threat into an active weapon. VulnCheck recently detected active exploitation of CVE-2026-66066. The cybersecurity community commonly refers to this severe flaw as KindaRails2Shell....
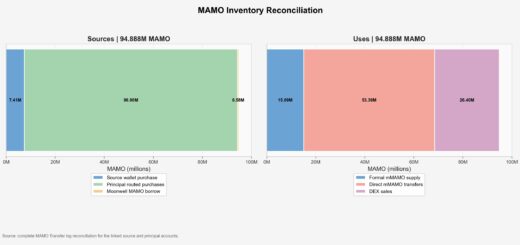
An attacker turned the comparatively small market for the MAMO token into a source of multimillion-dollar loans. Within a few hours, the assailant inflated the value of collateral in Moonwell, borrowed $11 million in...
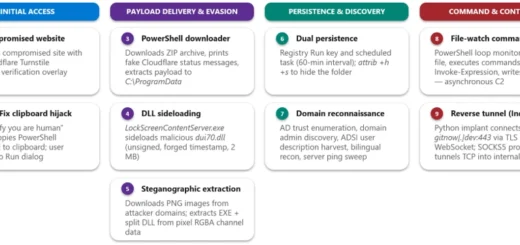
A familiar humanity check has suddenly become a gateway into the corporate network. Microsoft has disclosed a campaign named TerminalFix, in which compromised websites display a counterfeit Cloudflare Turnstile CAPTCHA and coax the visitor...
An enormous fragment of early Steam history suddenly became accessible for public scrutiny over a decade later. A colossal archive, spanning roughly 12 to 13 terabytes, is currently circulating rapidly across the internet. This...
The US Department of Justice has had to amend a resounding statement about the Chinese hacking group QTFY. After the first release, the impression formed that the attackers had successfully penetrated the networks of...
Malicious tools strive to blend into ordinary network traffic, but the new Miraak framework has gone further and transformed a cloud PostgreSQL database into a full-fledged channel for controlling infected computers. Blackpoint Cyber specialists...
A cyberattack on one of Australia’s largest book distributors has been disrupting deliveries across the country for roughly six weeks. After intruders breached the systems of Alliance Distribution Services, bookshops are receiving less stock,...
Open registration on developer platforms generally streamlines onboarding processes. However, concerning Gitea, this convenience inadvertently transformed a critical vulnerability into an easily accessible intrusion point. The Shadowserver Foundation recently identified a staggering 8,393 internet-facing...
ServiceNow recently addressed three maximum-severity vulnerabilities residing within its AI Platform. Astonishingly, each individual flaw received a perfect 10.0 rating on the CVSS 4.0 scale. Furthermore, a potential attacker requires absolutely no authentication or...
Malicious code no longer necessarily requires complex obfuscation to successfully evade neural network detection. Sometimes, merely inserting a specific phrase within a comment suffices. The artificial intelligence will subsequently refuse to continue its analysis...
Companies have only a few months left to fortify their defenses before AI markedly accelerates real-world cyberattacks. OpenAI issued that warning in an open letter endorsed by 128 organizations, among them Google, Microsoft, Anthropic,...