Mantax Otax Fuses Android Ransomware With Spyware
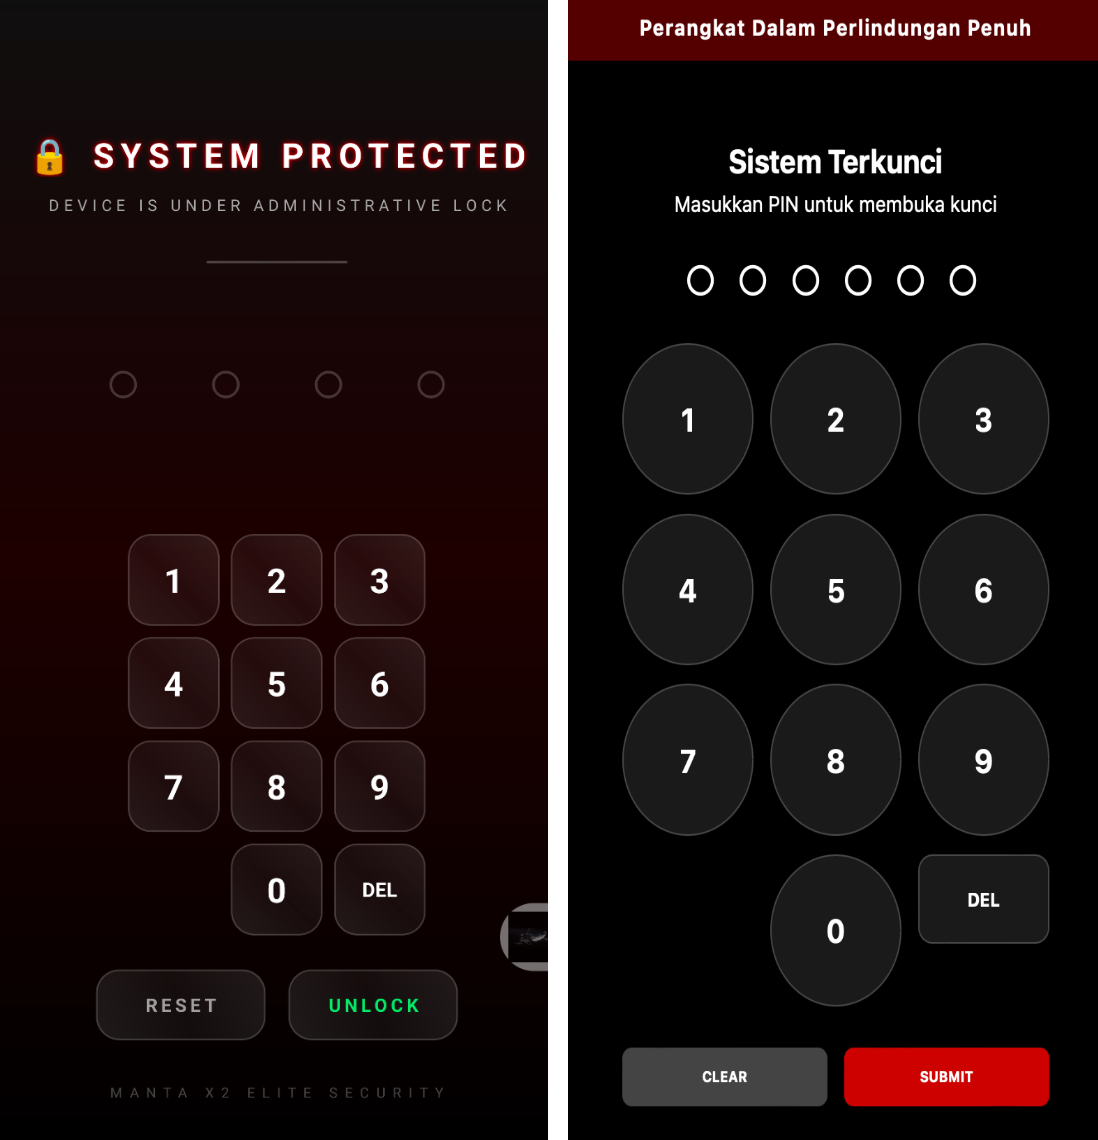
Android ransomware is no longer confined to locking files: Mantax Otax transforms an infected smartphone into a spying instrument and a channel of pressure on its owner at once. Zimperium has described the malware, which encrypts data on older versions of Android, intercepts SMS and one-time codes, records the screen, and, without the owner’s knowledge, takes photographs with both cameras. Zimperium’s analysis of Mantax Otax details the full campaign.
How It Spreads and Takes Hold
Mantax Otax is distributed as an APK through third-party file-sharing sites, links in messengers, and phishing messages. After installation, the program requests device administrator rights, access to SMS, contacts, audio, and images, and then attempts to obtain the Accessibility service. That service allows it to interact with the interface of other applications and broadens remote control.
Encryption That Targets Older Android
The encryptor is especially dangerous for Android 9 and older versions. Mantax Otax obtains a separate AES key for each infected device, recursively hunts for documents, archives, databases, media files, and cryptographic keys, deletes the originals, and saves encrypted copies with the .enc extension. On Android 10 and newer, Scoped Storage sharply limits access to shared storage.
Surveillance Runs Regardless of Encryption
The spyware component does not depend on the success of encryption. Mantax Otax monitors notifications and incoming SMS, gathers contacts, the call log, browser history, Google account data, and gallery files. The malware also attempts to extract WhatsApp correspondence and Telegram credentials, and through MediaProjection it takes screenshots, writes MP4 videos, and transmits the screen image in near real time.
Version Two Turns Up the Pressure
Operators can substitute the lock screen and intercept the entered PIN code. The second version of Mantax Otax gained new means of coercion: commands via WebSocket block applications and touches, bury the screen under windows, launch full-screen videos and images, and force the smartphone to speak a given text through the speech synthesizer. After encryption, a chat appears for negotiating the ransom.
Agile Infrastructure and Indonesian Targeting
Mantax Otax obtains the current domain of its command server from a GitHub repository, so operators can change the address without updating the APK. The first version used Firebase for commands; the new one switched to WebSocket. By linguistic markers and the files found, Zimperium links the campaign chiefly to targets in Indonesia. The company did not publish data on the number of infections.
How to Stay Protected
The publication advises against installing APKs from random messages and third-party file-sharing sites, and against granting unknown programs administrator rights, Accessibility, or access to SMS, the camera, and screen capture. At the first suspicion of infection, it is best to disconnect the smartphone from the network and review sensitive permissions. If the malware could have seen passwords or codes, they must be changed from a clean device.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


