CVE-2026-128138: NLTK Sandbox Bypass Fixed in 3.10.4
TL;DR
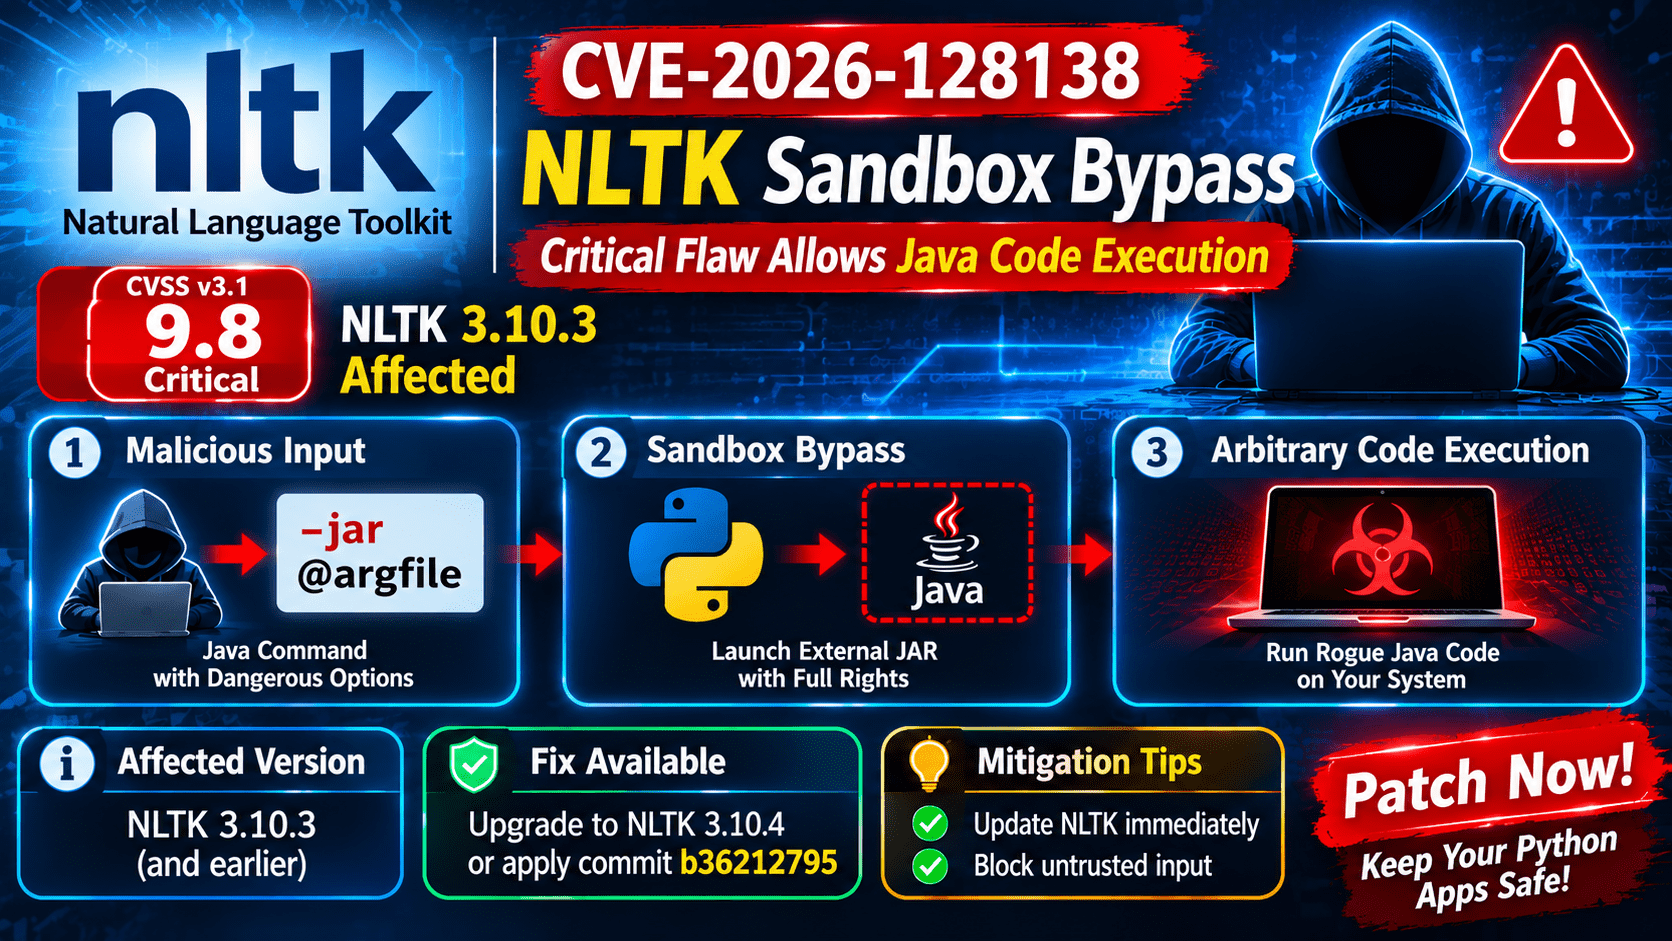
Maintainers of the Natural Language Toolkit (NLTK) disclosed CVE-2026-128138 on November 15, 2026. This critical NLTK Sandbox Bypass scores 9.8 on the CVSS v3.1 scale and stems from an incomplete fix in version 3.10.3. Attackers who control Java command inputs can bypass sandbox checks and run rogue Java code.
Why It Matters
Python devs and data teams use NLTK to parse text and run Java tools like Stanford Segmenter. Earlier, NLTK 3.10.3 added rules to block JVM argument bugs tracked as GHSA-m4rf-3fr8-xwx3 and CVE-2026-12841. However, researcher kokomaru167 found that the patch missed a second input path. Thus, any Python app passing user input to NLTK Java helpers stays open to code execution.
The GitHub security advisory includes a local reproducer script to verify the bypass. Still, no active attacks in the wild have been confirmed so far. Also, importing NLTK alone does not put a host at risk unless an app passes untrusted input to these Java calls.
How the Attack Works
Unchecked Launcher Tokens in java()
Tracked under CWE-77 and CWE-88, this NLTK Sandbox Bypass hits the nltk.internals.java() helper. In version 3.10.3, the tool checks the options list and blocks unsafe flags like -jar or @argfile. Next, it builds the final command by joining those options, the classpath, and the cmd list.
Sadly, the code does not check if the first item in cmd is a valid Java class name. Therefore, Java reads a leading -jar flag or @argfile token in cmd as a launcher switch.
Two Reachable API Paths
Researcher kokomaru167 proved two ways to trigger this flaw with default settings. First, an attacker can pass -jar as the first item in nltk.internals.java(cmd=...) to launch an outside JAR file. Second, the StanfordSegmenter wrapper puts its public java_class input at the start of the cmd list. Passing an @argfile token there forces Java to run an external JAR file. As a result, the child JVM runs rogue code with the full rights of the Python app.
Affected Versions
Vulnerable NLTK Builds
CVE-2026-128138 impacts the Python nltk package at version 3.10.3. Older builds like 3.10.2 also lack full sandbox blocks against outside classpath files.
Patch and Mitigation Steps
Developers merged pull request #3771 (commit b36212795) on the develop branch to close this NLTK Sandbox Bypass. The fix raises a ValueError if the first cmd item starts with a dash or @ sign. Moreover, it blocks any cmd token that uses an @argfile path. Teams should update to NLTK 3.10.4 or apply commit b36212795 right away. Meanwhile, devs must block raw user input from reaching java(cmd=...) or StanfordSegmenter(java_class=...).
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal