Category: Vulnerability

OnePlus smartphone displaying a root access vulnerability alert with OxygenOS logo 0

OnePlus Threatens Researcher Over Unpatched Root Flaw

OnePlus recently received a comprehensive forensic report detailing a devastating vulnerability chain within OxygenOS. This critical flaw empowers an entirely unprivileged, standard Android application to seamlessly achieve root access without requesting a single user...

CISA Known Exploited Vulnerabilities catalog listing for SharePoint and WSO2 0

CISA Catalogs Exploited Vulnerabilities Across Major Platforms

The United States Cybersecurity and Infrastructure Security Agency (CISA) recently expanded the CISA Known Exploited Vulnerabilities catalog, adding four critical flaws currently being weaponized in active, real-world cyberattacks. These devastating threats compromise Microsoft SharePoint...

Elementor WordPress plugin interface highlighting a CSRF vulnerability exploit 0

Critical Elementor CSRF Vulnerability Threatens Millions

A seemingly innocuous link possesses the terrifying potential to transform an active WordPress administrator session into a devastating site takeover mechanism. Cybersecurity researchers recently unearthed a profound vulnerability within the ubiquitous Elementor Website Builder....

Cloudflare Containers infrastructure diagram showing cross-tenant data vulnerability and thin provisioning 0

Cloudflare Resolves Cross-Tenant Data Exposure Flaw

A terminated container is theoretically engineered to vanish entirely, alongside all its ephemeral data. However, within Cloudflare’s sprawling infrastructure, fragments of this sensitive information inexplicably survived the previous owner of the physical disk block....

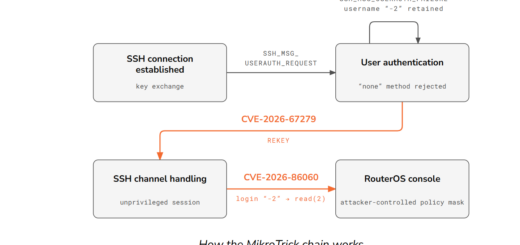
CERT Polska AI analysis laboratory analyzing MikroTik RouterOS binary files 0

CERT Polska Dissects the MikroTrick RouterOS Exploit

Following MikroTik’s abrupt release of an emergency security update, the elite CERT Polska team required approximately one hour of forensic analysis to pinpoint the underlying critical vulnerability. By meticulously scrutinizing the architectural modifications within...

F5 BIG-IP Access Policy Manager vulnerability and CISA KEV catalog warning 0

Active Zero-Day Attacks Target F5 BIG-IP Gateways

Penetrating an enterprise F5 corporate gateway may no longer require a compromised password or even a valid user account. The manufacturer recently disclosed a catastrophic vulnerability embedded within the BIG-IP Access Policy Manager (APM),...

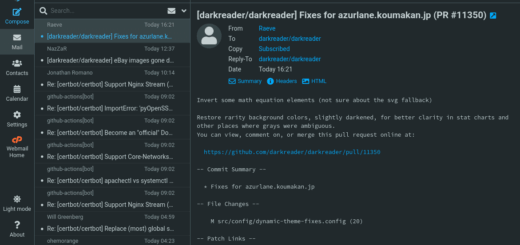
Roundcube Webmail login interface depicting an active SQL injection vulnerability 0

Active Exploitation Targets Roundcube Webmail Servers

A critical vulnerability can easily outlive its official patch if system administrators fail to update their servers expeditiously. Precisely this perilous scenario is currently unfolding surrounding the widely deployed Roundcube Webmail platform. Malicious actors...