GitHub has successfully rewritten the entire Copilot runtime environment, transitioning from TypeScript to Rust. Astonishingly, Copilot’s own artificial intelligence agents generated the vast majority of this new codebase. This monumental migration consumed approximately three...
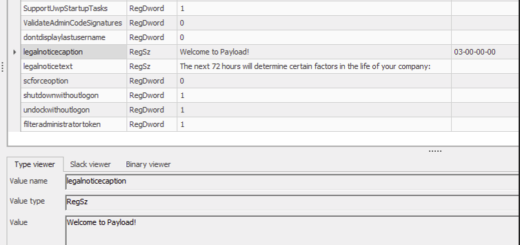
The PAYLOAD extortion operators recently targeted a Middle Eastern manufacturing enterprise without executing a single encryptor payload on any Windows machine. After successfully acquiring domain administrator privileges, the malicious actors weaponized Active Directory Group...
The intense controversy surrounding LG Smart TVs did not erupt over a single, disputed toggle switch. Instead, the debate ignited over the nebulous boundary separating perceived “constant eavesdropping” and the undeniable reality of automated...
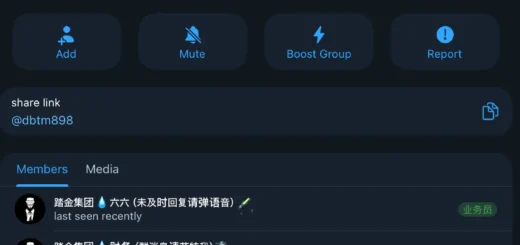
Chinese cybercriminals increasingly abandon the traditional dark web infrastructure. Operations involving sophisticated phishing campaigns, stolen credit card trafficking, money laundering, and the recruitment of accomplices have migrated overwhelmingly to Telegram. Within this messaging platform,...
Four severe vulnerabilities deeply embedded within the Linux kernel, lurking undetected for 10 to 21 years, finally have functional public exploits. Consequently, these critical flaws allow attackers to achieve root privilege escalation. These vulnerabilities...
The prominent cybersecurity firm CrowdSec recently acknowledged a significant data breach. Attackers successfully exfiltrated source code from approximately 170 private GitHub repositories. A malicious actor initially duplicated this proprietary code on May 22, 2026....
An attempt to download a film through a familiar torrent tracker could infect a computer even without the tracker itself being hacked. Attackers compromised iTorrents.org, a popular repository of torrent files, and made the...
Extortion has suddenly turned against the extortionists themselves. ShinyHunters gained access to the Tor site of the Clop group and replaced its content with a page of its own. BleepingComputer confirmed that the attackers...
A single link in an attacker’s hands can make WordPress install a theme without a button being pressed, provided an already-authenticated administrator opens it. On September 17, WordPress released version 7.1.1, which closes a...
Firefox recently received one of its most substantial security packages in recent history. Within the Firefox 156 release, Mozilla decisively remediated an astonishing 73 vulnerabilities. This formidable list encompassed dozens of vectors allowing for...
Although a patch for the critical VMware vCenter vulnerability has existed since late July, the situation escalated into a significantly more perilous phase over the subsequent six weeks. The Cybersecurity and Infrastructure Security Agency...
Adversaries have ingeniously manipulated Google Docs to perform a function utterly unexpected from a cloud-based word processor: they transformed a standard document into an interactive malware installation vector. Following the conclusion of the prestigious...