KillSec Ransomware Group Taken Down in Europol Raid
A Ransomware Gang With a Teenage Boss
Even the extortion business turns out to have surprisingly young leadership. The international Operation KillSwitch has crippled the infrastructure of KillSec. Investigators believe the group’s main operator is a 16-year-old.
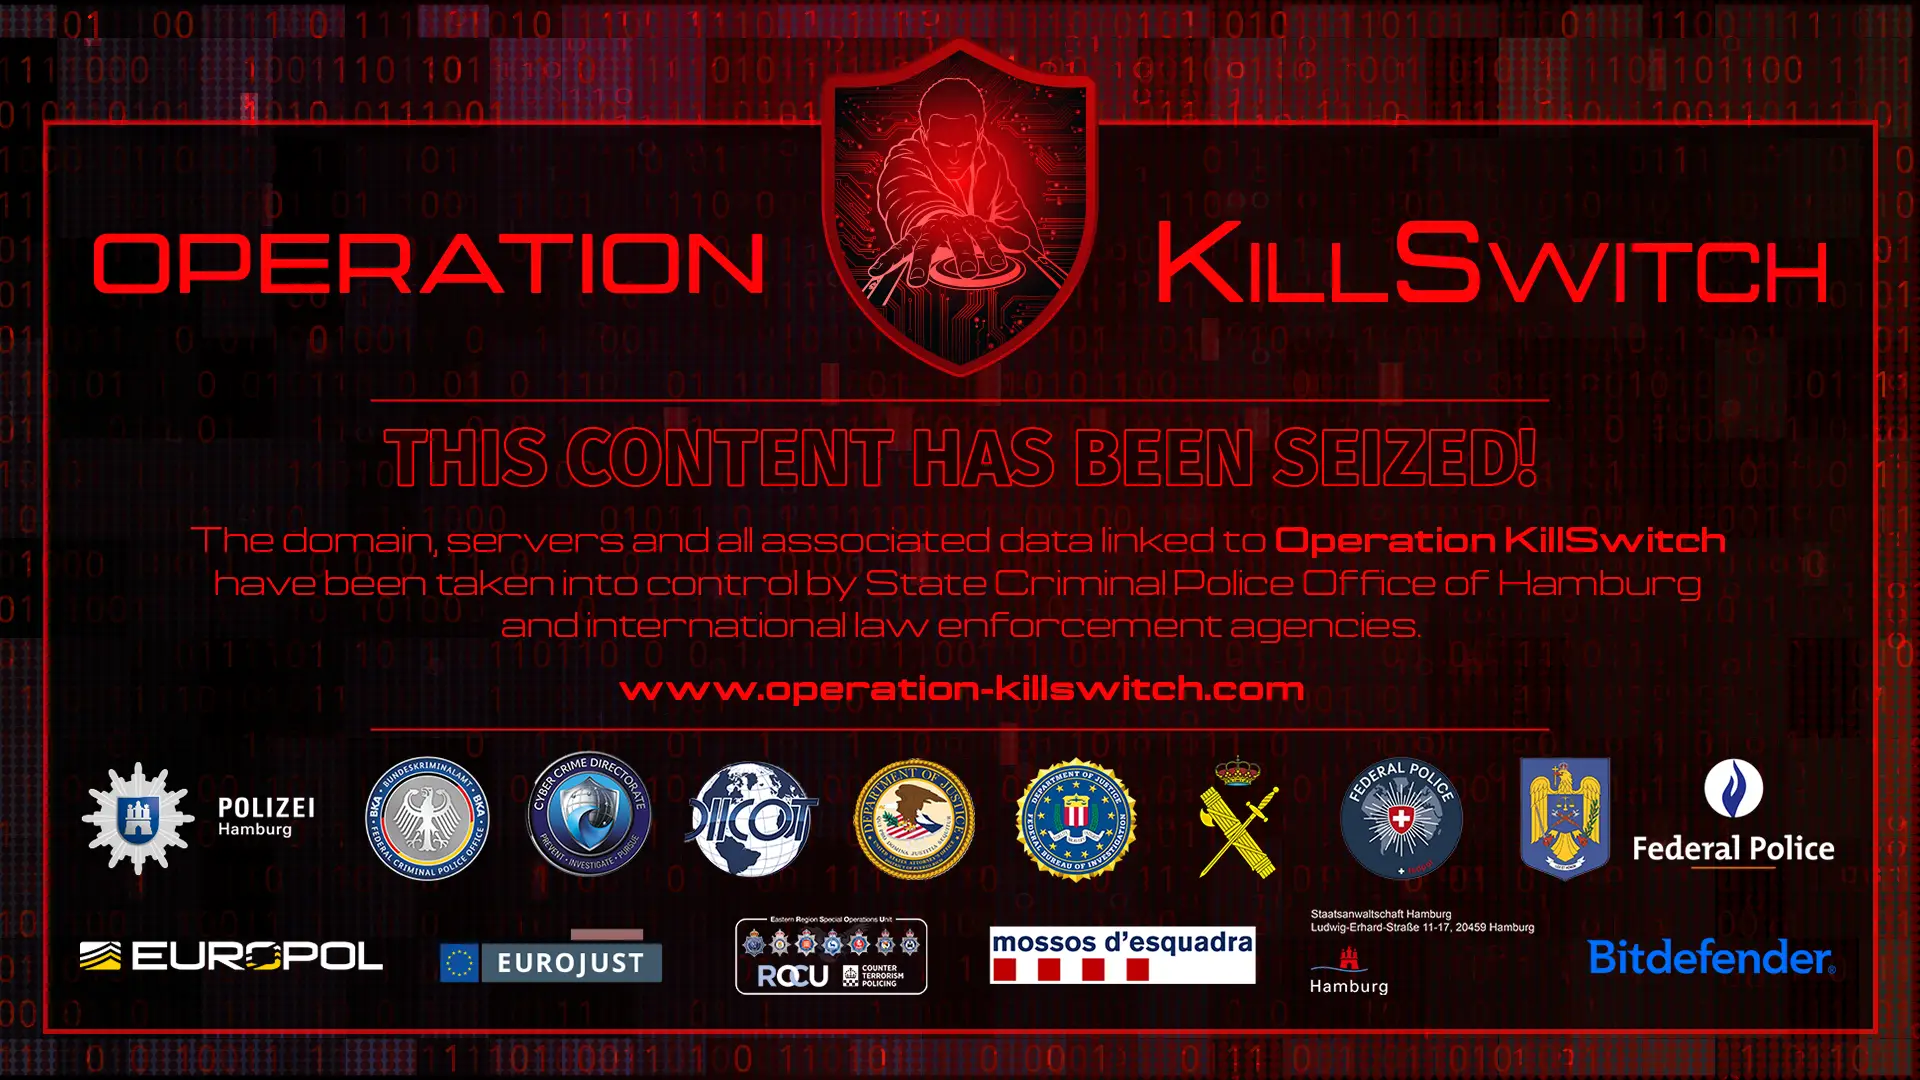
On September 30, law enforcement detained three suspects. They also carried out eight searches in four countries and seized the group’s leak site.
The Scale of the Investigation
Europol said the probe covers about 1,000 alleged attacks worldwide. Roughly 500 of them are already deemed successful. That number may change once experts examine the seized devices and servers.
KillSec has operated since about 2024. The investigation began in early 2025.
Who Is Behind the Group
Investigators consider a 16-year-old suspect the main operator and administrator of KillSec. Another participant is linked to building the infrastructure. He turned 18 in August 2026, and he was a minor during part of the alleged crimes.
Police also identified a suspected negotiator and an affiliate. The search for other members continues.
How KillSec Attacked Its Victims
KillSec broke into organizations through software vulnerabilities and poorly protected access points. Cloud storage was a special target.
After a breach, the attackers copied confidential data to their own infrastructure. They then threatened to publish the files unless the victim paid. If the victim refused, the data could appear on the leak site for free.
A RaaS Model Aided by AI
The scheme combined central infrastructure with the split of roles typical of ransomware-as-a-service (RaaS). In 2026, the Qilin group also grew a similar model. There, operators maintain the platform, while affiliates run the attacks and share the ransom.
In the KillSec case, investigators also found that members used AI. They used it to support the infrastructure and to find potential targets.
What Operation KillSwitch Seized
During KillSwitch, officers took control of five central KillSec servers. They include command systems and storage for stolen files.
The group’s domains now redirect to a seizure notice. Access to at least 110 TB of stolen data is blocked for outsiders. Earlier, the shutdown of RAMP showed how a police operation can reshape the infrastructure of the ransomware ecosystem.
An Investigation Still Under Way
The inquiry is not finished. Officers are studying computers, servers, and other media. They are also tracing criminal proceeds, including cryptocurrency. The material may reveal more attacks, victims, and KillSec members.
For now, the confirmed result is clear. The group’s infrastructure is seized. Three people are detained. Most importantly, the key blackmail site no longer sits under KillSec control.
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal


