Tagged: Gitlab

Ruby regex vulnerabilities diagram showing Onigmo memory corruption and GitLab RCE exploit chain 0

Ruby Regex Vulnerabilities Trigger Critical GitLab RCE

The core maintenance team behind the Ruby programming language has released versions 4.0.9, 3.4.12, and 3.3.13. Specifically, these critical updates resolve severe vulnerabilities within the embedded Onigmo regular expression parsing engine. These underlying memory...
GitLab interface with a warning overlay indicating active vulnerability exploitation 0

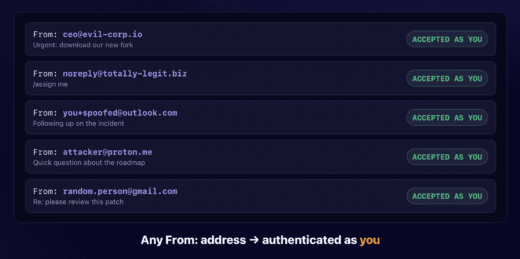
Critical GitLab Flaw Transitions to Active Global Threat

A critical GitLab vulnerability, bearing the maximum possible CVSS score of 10, has officially transitioned from a theoretical urgent update into a verified, real-world threat. The Cybersecurity and Infrastructure Security Agency (CISA) definitively confirmed...