Information Security News Blog
HP’s native BIOS firmware has historically exhibited notable operational instability. Consequently, many users encounter severe system issues after deploying mandatory firmware updates. Recently, numerous operators experienced abrupt boot interruptions or catastrophic black-screen system freezes....
The Mozilla Foundation recently distributed an essential maintenance release for the Firefox v151 series. Consequently, this deployment addresses a multitude of software regressions resulting from recent architectural overhauls. Therefore, the vendor has accelerated its...
Intel is currently architecting an elegant communication framework for the Linux ecosystem. This innovation bridges adjacent workstations directly via USB4 or Thunderbolt media, bypassing traditional network configuration matrices entirely. Consequently, this point-to-point architecture facilitates...
Microsoft recently initiated the distribution of its May “C” preview update for Windows 11. This release serves as an early testing vehicle for upcoming capabilities. Consequently, these components will undergo validation before merging into...
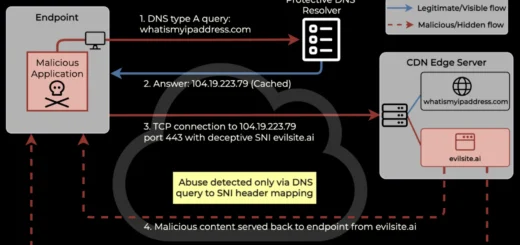
The cybersecurity researchers at ADAMnetworks recently unveiled a novel evasion technique. This method allows malicious data packets to conceal themselves behind trusted domains and Content Delivery Networks (CDNs). Consequently, this development threatens organizations relying...
Researchers have unearthed a critical security vulnerability within the ubiquitous 7-Zip data compression utility. Opening a meticulously engineered disk image triggers arbitrary remote code execution rather than a standard decompression failure. Crucially, this memory...
Perimeter Compromise and Systemic Risk LiteSpeed recently resolved a critical privilege escalation vulnerability within its user-facing cPanel plugin. This severe security defect is tracked globally as CVE-2026-48172. Threat actors are already exploiting this flaw...
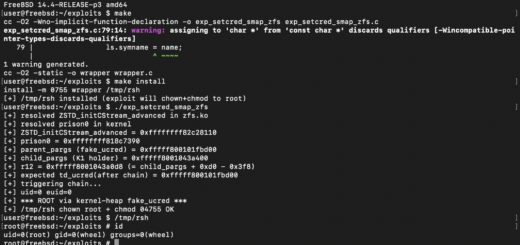
The FreeBSD security apparatus has successfully resolved a high-severity vulnerability, cataloged as CVE-2026-45250, within the setcred(2) system call architecture. This fundamental defect resided within the core kernel logic, empowering an unauthenticated local adversary to...
Microsoft has issued a cautionary directive to proprietors of Windows 11 ecosystems: failure to transition computational hardware to the modernized Secure Boot cryptographic certificates prior to June 2026 will not precipitate catastrophic boot failures;...
The Verus project has successfully reclaimed most of its capital following the recent cryptographic bridge exploit. The community reported that the attacker returned 4,052.4 ETH. Consequently, the team now controls approximately 75% of the...
The algorithmic stablecoins EURR and USDR, curated by the digital asset institution StablR, suffered a severe and precipitous de-pegging from their respective fiat baselines following a targeted compromise of their token-minting contract within the...
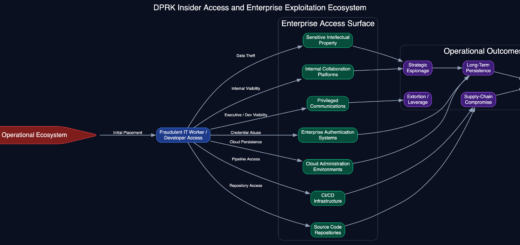
North Korea’s adversarial presence within the digital theater has transcended the legacy paradigm of isolated, decentralized hacking collectives. Per comprehensive threat intelligence compiled by Krypt3ia, the state’s offensive cyber apparatus has evolved into a...