Author: Nam Phong

Apple Find My hack showing location tracking data on a Linux terminal interface 0

Apple Find My Hack: Location Tracking on Linux

An enterprising researcher successfully compelled Apple Find My to operate within an environment completely unsupported by the corporation. A 22-year-old security specialist, operating under the pseudonym Zerotistic, cleverly registered a Linux machine within Apple’s...

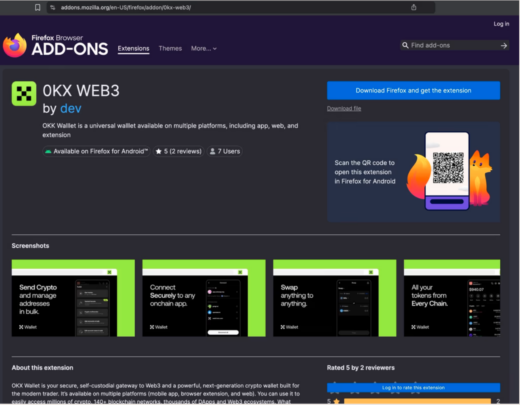
Malicious Firefox extensions stealing cryptocurrency 0

Malicious Firefox Extensions Steal Crypto Passwords

Security experts unearthed dozens of counterfeit Firefox extensions. These malicious add-ons masqueraded as cryptocurrency wallets and standard utilities. Some programs appeared innocuous for months. Following an update, they transformed into sinister tools. They actively...

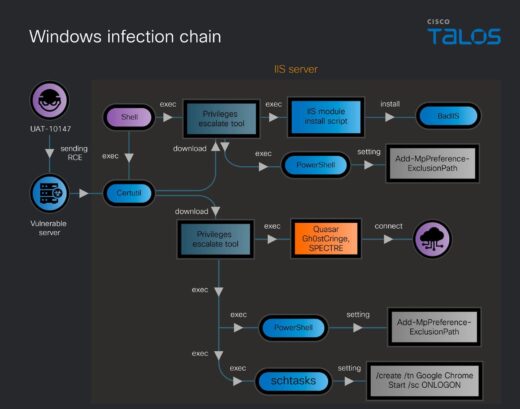
UAT-10147 hacker group deploying SPECTRE backdoor using AI-driven attack vectors 0

UAT-10147 Hackers Use AI to Deploy SPECTRE Backdoor

A sophisticated Chinese-speaking hacker collective, designated UAT-10147, has weaponized artificial intelligence, transforming it from a rudimentary coding assistant into a formidable attack instrument. These malicious actors deploy AI agents to hunt for vulnerabilities, forge...

ToxicPanda Android banking trojan stealing PINs on a smartphone screen 0

ToxicPanda Android Banking Trojan: 2.0 Upgrade

The notorious banking trojan ToxicPanda has resurfaced in a significantly more formidable iteration. ToxicPanda 2.0 now possesses the capability to pilfer PINs from banking and cryptocurrency applications. It intercepts smartphone lock passwords with alarming...

Mabna Institute Iranian hackers cyber theft campaign targeting global universities and intellectual property 0

17 Iranians Indicted for Massive Cyber Theft Campaign

Over 100,000 educators globally fell victim to relentless hackers who spent years plundering academic research, proprietary books, and other invaluable intellectual property. The United States indicted 17 Iranian nationals affiliated with the Mabna Institute...

C2Looper backdoor malware execution flow and GitHub command and control structure 0

C2Looper Backdoor Malware Uses GitHub for C2

Security specialists at Zscaler have unearthed a novel backdoor dubbed C2Looper, which malicious actors presumably deploy as a precursor to devastating ransomware assaults. This pernicious software enables adversaries to establish a clandestine foothold within...