Information Security News Blog
-
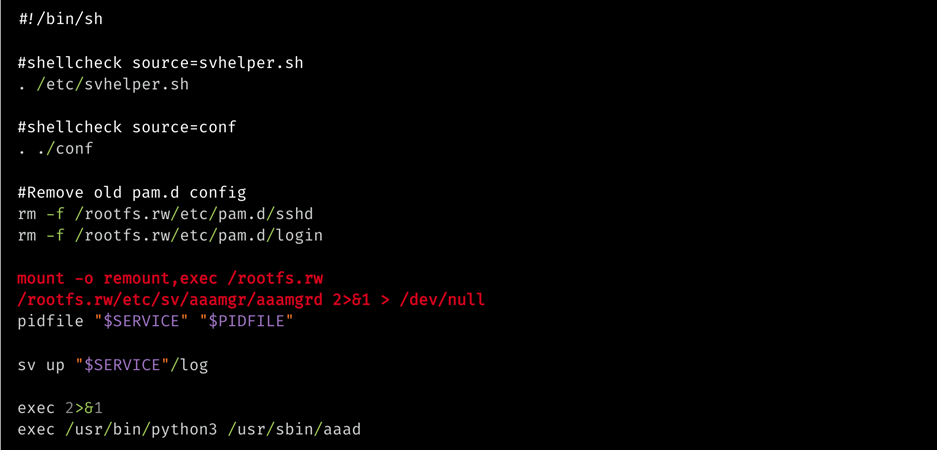
State-sponsored threat actors are compromising critical enterprise network infrastructure. Specifically, operators tracking as UAT-11473 breached Cisco Catalyst SD-WAN controllers across strategic industries. Intruders deployed a sophisticated in-memory malware suite dubbed KeyDrift into active system...
-
Unidentified cybercriminals breached internal digital infrastructure at Belgium’s Federal Public Service Finance during the night of October 28. Defense monitoring tools detected the unauthorized intrusion within hours. Consequently, system administrators took immediate defensive countermeasures...
-
TL;DR CrowdStrike identified a major cyber espionage push called the VAPOR PANDA ARTEX campaign targeting over 200 global entities. The adversary ran the ARTEX framework alongside DeepSeek language models to conduct multiple parallel network...
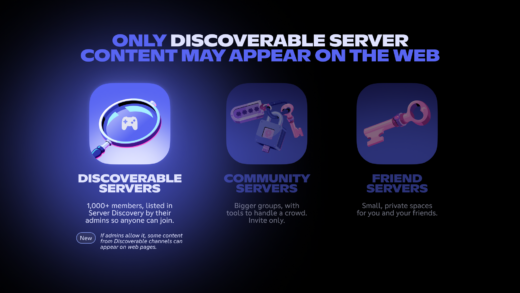
Private digital discussions historically confined to community servers will soon surface across public web queries. Specifically, the newly announced Discord search indexing initiative exposes select community conversations to public search engines. This structural transition...
Cybersecurity investigators recently uncovered a sophisticated multi-stage intrusion against government-affiliated infrastructure. Specifically, adversaries compromised a public management portal to infiltrate internal enterprise networks. Consequently, the attackers breached twenty-five servers across sensitive environments. According to...
Threat actors are actively weaponizing a zero-day flaw in enterprise security appliances. Specifically, this zero-day targets the Cisco firewall DoS vulnerability across popular hardware lines. Attackers can trigger sudden device reboots remotely. Furthermore, these...
A cascade of fourteen security flaws across Linux and FreeBSD opened dangerous pathways to root privileges. Specifically, these flaws facilitate container escapes, virtual machine breakouts, and remote kernel code execution. Furthermore, functional exploits already...
Enterprise servers face severe compromise before operating systems even initialize through meticulously crafted network packets. Specifically, security researchers uncovered a catastrophic TianoCore UEFI vulnerability that enables remote takeover prior to standard defensive execution. The...
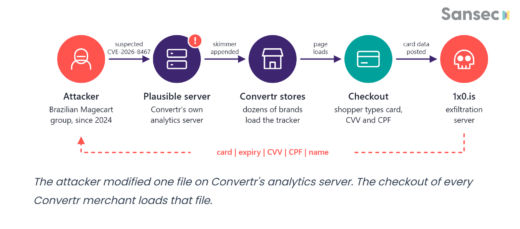
A solitary compromised file allowed cybercriminals to harvest credit card data across dozens of prominent Brazilian retailers. Specifically, the malicious actors embedded an invisible digital skimmer inside a routine analytics script. The infected script...
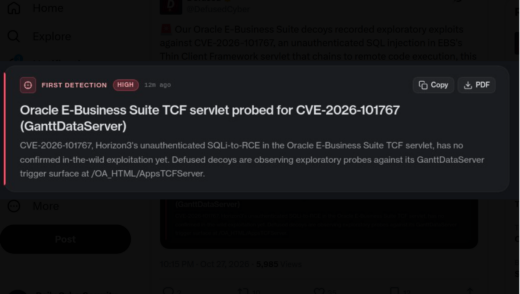
Threat actors began scanning enterprise networks almost immediately after software maintainers published defensive fixes. Specifically, cybersecurity analysts detected exploratory probes targeting the severe Oracle EBS vulnerability on research honeypots. The security firm Defused recorded...
TL;DR Maintainers of the LabStack Echo Go framework disclosed a critical access control bypass vulnerability tracked as CVE-2026-118264 (CVSS v4.0: 9.1). The flaw allows unauthenticated attackers to bypass route-level authentication and authorization middleware via...
TL;DR SignalWire disclosed three critical FreeSWITCH vulnerabilities on October 28, 2026, impacting SIP chat handling, WebSocket frame parsing, and ICE media verification. The most severe flaw, CVE-2026-116779 (CVSS 9.8), allows remote command execution via...
Even a successful device verification cannot guarantee absolute cryptographic legitimacy. Recently, hardware wallet manufacturer Keystone confirmed a severe intrusion into its administrative website. Specifically, threat actors purloined a foundational factory WebAuth key during the...
Japanese technology giant GMO Internet issued an unprecedented emergency advisory to its subscribers. Specifically, the corporation urged clients to disconnect desktop computers, sever internet connections, and unplug power cables immediately. This drastic warning followed...
A rogue penetration tester orchestrated a devastating cyber offensive across South Korea alongside six accomplices. Specifically, the syndicate exfiltrated 8.2 million sensitive records from more than ninety domestic organizations. To accelerate the breach, the...