vesta: Docker and Kubernetes cluster configuration detect toolkit
Vesta
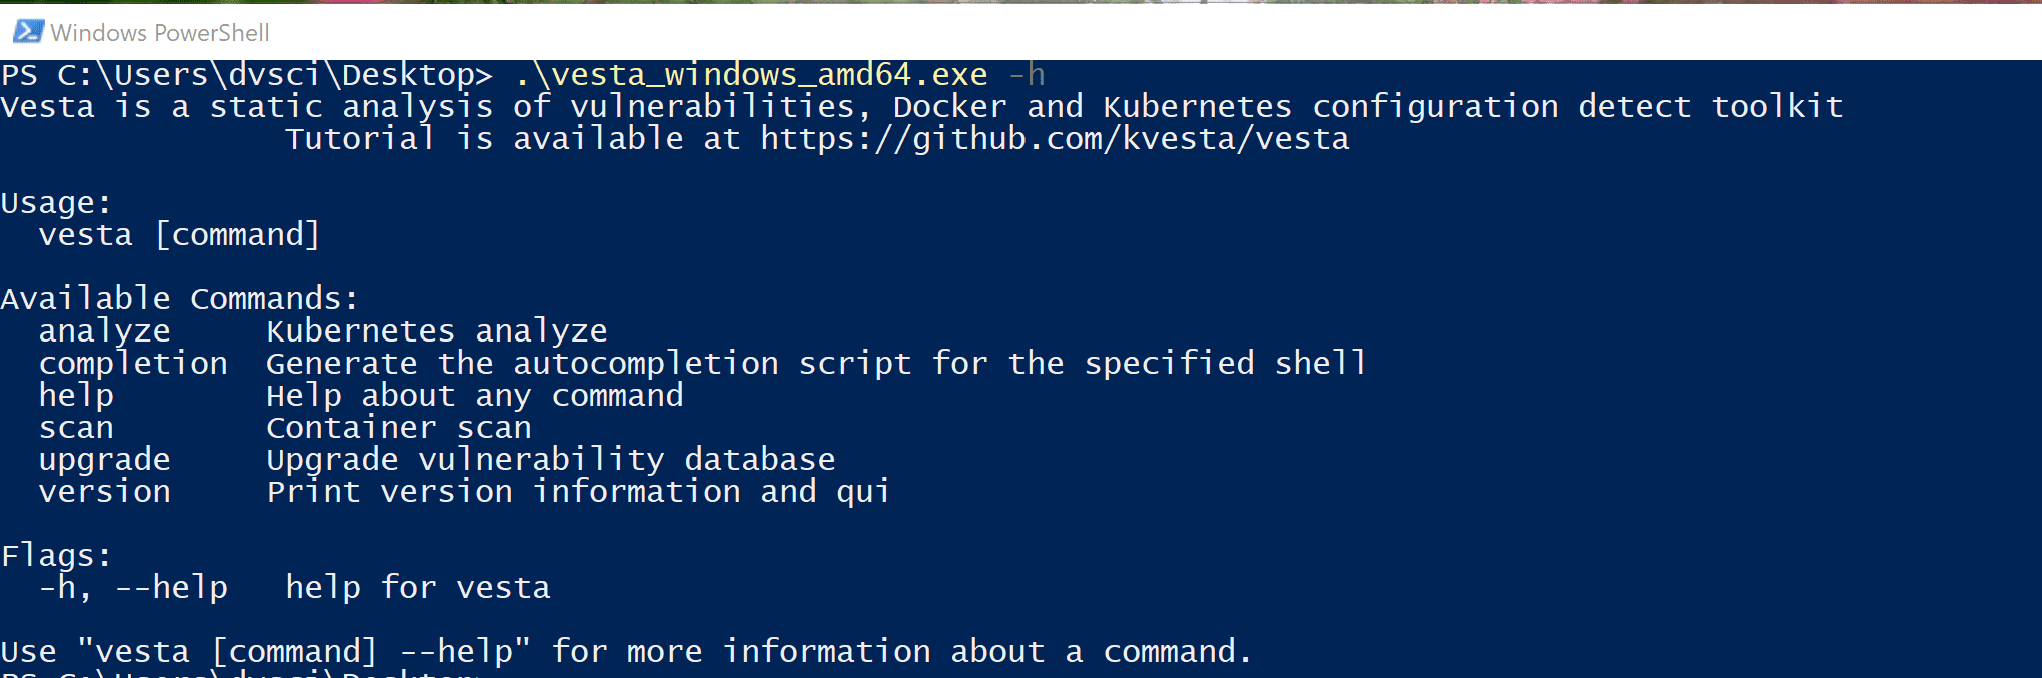
Vesta is a static analysis of vulnerabilities, Docker, and Kubernetes cluster configuration detect toolkit. It inspects Kubernetes and Docker configures cluster pods and containers with safe practices. It also analyses image or container components with an extra python module and node npm scan.
Vesta is a flexible toolkit that can run on physical machines in different types of systems (Windows, Linux, MacOS).
Checklist
Scan
- Support scanning input
- image
- container
- filesystem
- vm (TODO)
- Scan the vulnerabilities of major package managements
- apt/apt-get
- rpm
- yum
- dpkg
- Scan malicious packages and vulnerabilities of language-specific packages
- Java(Jar, War. major library: log4j)
- NodeJs(NPM, YARN)
- Python(Wheel, Poetry)
- Golang(Go binary)
- PHP(Composer, major frameworks: laravel, thinkphp, wordpress, wordpress plugins etc)
- Rust(Rust binary)
- Others(Others vulnerable which will cause a potential container escape and check suspicious poison image)
Docker
| Supported | Check Item | Description | Severity | Reference |
|---|---|---|---|---|
| ✔ | PrivilegeAllowed | Privileged module is allowed. | critical | Ref |
| ✔ | Capabilities | Dangerous capabilities are opening. | critical | Ref |
| ✔ | Volume Mount | Mount dangerous location. | critical | Ref |
| ✔ | Docker Unauthorized | 2375 port is opening and unauthorized. | critical | Ref |
| ✔ | Kernel version | Kernel version is under the escape version. | critical | Ref |
| ✔ | Network Module | Net Module is host and containerd version less than 1.41. |
critical/medium | |
| ✔ | Pid Module | Pid Module is host. |
high | |
| ✔ | Docker Server version | Server version is included the vulnerable version. | critical/high/ medium/low | |
| ✔ | Docker env password check | Check weak password in database. | high/medium | |
| ✔ | Docker History | Docker layers and environment have some dangerous commands. | high/medium | |
| ✔ | Docker Backdoor | Docker env command has malicious commands. | critical/high | |
| ✔ | Docker Swarm | Docker swarm has dangerous config or secrets or containers are unsafe. | medium/low | |
| ✔ | Docker supply chain | Docker supply chain has vulnerable configurations | critical/high/ medium | Ref |
Kubernetes
| Supported | Check Item | Description | Severity | Reference |
|---|---|---|---|---|
| ✔ | PrivilegeAllowed | Privileged module is allowed. | critical | Ref |
| ✔ | Capabilities | Dangerous capabilities are opening. | critical | Ref |
| ✔ | PV and PVC | PV is mounted the dangerous location and is active. | critical/medium | Ref |
| ✔ | RBAC | RBAC has some unsafe configurations in clusterrolebingding or rolebinding. | high/medium/ low/warning | |
| ✔ | Kubernetes-dashborad | Checking -enable-skip-login and account permission. |
critical/high/low | Ref |
| ✔ | Kernel version | Kernel version is under the escape version. | critical | Ref |
| ✔ | Docker Server version (k8s versions is less than v1.24) | Server version is included the vulnerable version. | critical/high/ medium/low | |
| ✔ | Kubernetes certification expiration | Certification is expired after 30 days. | medium | |
| ✔ | ConfigMap and Secret check | Check weak password in ConfigMap or Secret. | high/medium/low | Ref |
| ✔ | PodSecurityPolicy check (k8s version under the v1.25) | PodSecurityPolicy tolerates dangerous pod configurations. | high/medium/low | Ref |
| ✔ | Auto Mount ServiceAccount Token | Mounting default service token. | critical/high/ medium/low | Ref |
| ✔ | NoResourceLimits | No resource limits are set. | low | Ref |
| ✔ | Job and Cronjob | No seccomp or seLinux are set in Job or CronJob. | low | Ref |
| ✔ | Envoy admin | Envoy admin is opening and listen to 0.0.0.0. |
high/medium | Ref |
| ✔ | Cilium version | Cilium has vulnerable version. | critical/high/ medium/low | Ref |
| ✔ | Istio configurations | Istio has vulnerable version and vulnerable configurations. | critical/high/ medium/low | Ref |
| ✔ | Kubelet 10250/10255 and Kubectl proxy | 10255/10250 port are opening and unauthorized or Kubectl proxy is opening. | high/medium/low | |
| ✔ | Etcd configuration | Etcd safe configuration checking. | high/medium | |
| ✔ | Sidecar configurations | Sidecar has some dangerous configurations. | critical/high/ medium/low | |
| ✔ | Pod annotation | Pod annotation has some unsafe configurations. | high/medium/ low/warning | Ref |
| ✔ | DaemonSet | DaemonSet has unsafe configurations. | critical/high/ medium/low | |
| ✔ | Backdoor | Backdoor Detection. | critical/high | Ref |
| ✔ | Lateral admin movement | Pod specifics a master node. | medium/low |
Download
Support Our Threat Intelligence
If you find our technology report and cybersecurity news helpful, consider supporting our work.
 Buy Me a Coffee
PayPal

USDT (TRC20):
TN8BdV8cp4T1Cd28gK9qTAnZknzzuwyUtm
USDT (ERC20):
0x3725e1a7d3bc5765499fa6aaafe307fabcd75bce


