Tagged: authentication bypass
Malicious actors have commenced active attacks against Citrix NetScaler infrastructure. They are exploiting the critical vulnerability designated as CVE-2026-19490. This severe flaw enables remote adversaries to circumvent authentication protocols entirely. Consequently, they gain illicit...
Corporate email can fall into an attacker’s hands after the compromise of a single low-privilege account. Nearly 22,000 internet-facing Microsoft Exchange servers have not received the fix for CVE-2026-62911, a flaw that allows every...
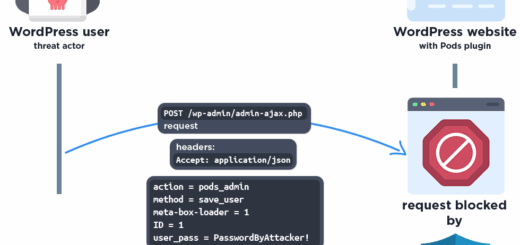
A WordPress site administrator’s password could be changed by an attacker without ever logging in. A critical vulnerability in the popular Pods plugin allowed an unauthenticated outsider to bypass several layers of security checks...
Attackers have begun exploiting a critical vulnerability in macOS’s built-in Screen Sharing feature to gain access to Mac computers without any valid credentials whatsoever. In several confirmed cases, attackers who established this unauthorized connection...
TL;DR Broadcom has patched five flaws across VMware ESX, vCenter, Workstation, and Fusion. Two of them form a critical VMware vCenter vulnerability pair, each rated 9.8 CVSS. One lets an attacker bypass authentication; the...
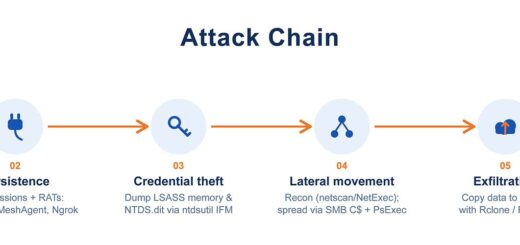
A single vulnerable VPN gateway can lay open an entire corporate network. Affiliates of the Qilin extortion group are already turning a fresh PAN-OS GlobalProtect flaw to precisely that purpose. Arctic Wolf specialists have...
Old internet forums may no longer sit at the center of digital life, but many continue to hold private messages, restricted sections, and accounts carrying years of personal history. A critical vulnerability discovered in...
Adversaries initiated a targeted reconnaissance campaign against vulnerable PraisonAI nodes less than four hours following the public disclosure of a critical security defect. An automated scanning entity identifying as CVE-Detector/1.0 launched offensives against exposed...
WordPress websites have once again fallen under siege due to a critical flaw in a popular extension. On this occasion, adversaries have targeted Burst Statistics—an analytics plugin deployed across approximately 200,000 web resources. The...
The Cybersecurity and Infrastructure Security Agency (CISA) of the United States has concurrently appended a triad of vulnerabilities to its Known Exploited Vulnerabilities catalog—a repository exclusively reserved for security aberrations actively weaponized by digital...
A critical vulnerability has been unearthed within the widely utilized Java authentication library, pac4j-jwt, empowering a malicious actor to masquerade as any system user, administrators included. This severe flaw has been designated the identifier...
A critical vulnerability has been unearthed within a ubiquitous component of supercomputing clusters, having resided surreptitiously within the source code for nearly two decades. This flaw empowers a local adversary to exfiltrate the secret...