Category: Malware

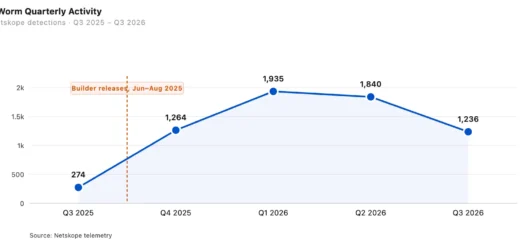
XWorm malware plugins architecture and Windows ResetSurvival remote access trojan analysis 0

XWorm Malware Plugins Survive Windows Factory Resets

XWorm has crossed a critical threshold where a conventional Remote Access Trojan (RAT) begins operating like a comprehensive pocket surveillance suite. Recently, Netskope Threat Labs identified four distinct variants of the malware circulating actively...
macOS Claude malvertising attack redirect chain 0

macOS Claude Malvertising Attack Uses Bing Redirects

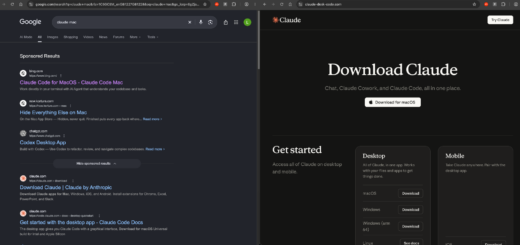
Threat actors have weaponized Google advertisements and Bing’s redirection architecture, forging an elaborate snare for macOS users seeking the Claude application. Analysts have unearthed a sophisticated paradigm wherein a promotional result for the query...

GhostAction attack compromised developer accounts GitHub supply chain 0

GhostAction Hack Compromises GitHub Developer Accounts

Malicious actors operating the GhostAction campaign successfully compromised two GitHub developer accounts. Within mere hours, they stealthily injected malicious scripts into a staggering minimum of 345 repositories. These insidious scripts systematically pilfered tokens and...

Custom ChatGPT bot interface mimicking a service error to trigger the ClickFix RAT infection chain 0

ClickFix RAT Disguised as Custom ChatGPT Bot Strikes

The most compelling element of this novel cyberattack resides not upon a disparate phishing domain, but directly within the authentic ChatGPT interface. Huntress unveiled a sophisticated campaign wherein adversaries engineered custom GPTs, masquerading them...

Conceptual visualization of a self-replicating prompt injection worm propagating between AI agents 0

The Emergence of Self-Replicating Prompt Injection Worms

Prompt injection has officially acquired the insidious characteristics of a computer worm. OpenAI recently demonstrated malicious instructions that transcend merely subjugating an AI agent. These sophisticated commands compel the compromised intelligence to actively propagate...

Citrix NetScaler architecture diagram showing DTLS vulnerability exploitation and WHIPSHOT deployment 0

Citrix NetScaler Zero-Day Attacks Unleash WHIPSHOT Malware

Breaching a Citrix NetScaler via a zero-day vulnerability merely constitutes the inaugural phase of a sophisticated attack. Following successful infiltration, threat actors deploy previously uncatalogued implants, WHIPSHOT and SLAPSHOT. These insidious tools guarantee persistent...

Fake Cloudflare human verification screen utilizing ClickFix social engineering via third-party.com 0

Placeholder Domain Hijacked for ClickFix Campaigns

A mundane, ubiquitous example URL embedded within countless developer documentation files has horrifyingly metamorphosed into a live attack vector. The specific domain, third-party[.]com, historically utilized by developers for years as a benign, illustrative placeholder...