Category: Information Security
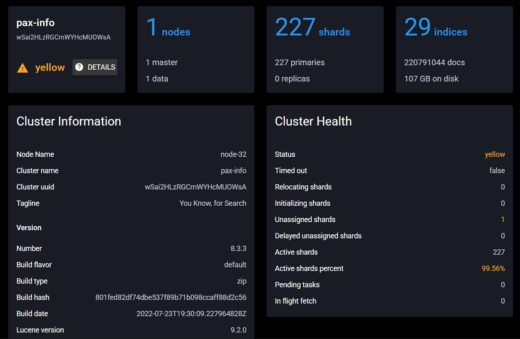
One of the most sensitive aviation databases proved to be guarded less securely than a rudimentary web service. On June 3, Kinryū Labs uncovered a staggering 220,783,700 records concerning passengers and flight crews within...
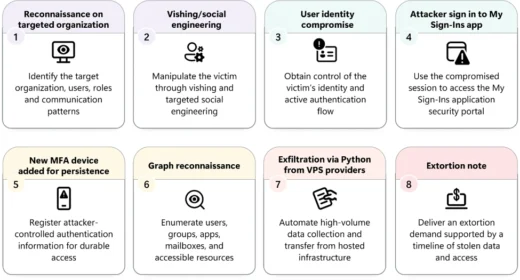
Passkeys were originally conceived as the ultimate cure for phishing, yet threat actors have ingeniously discovered a darker role for this technology. Currently, an attacker merely needs to telephone an employee while masquerading as...
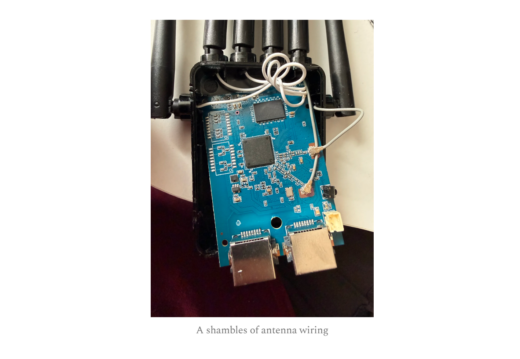
A Wi-Fi repeater costing a mere 3 pounds has emerged as a device harboring a pre-configured, concealed backdoor, effectively inviting complete system compromise. Penetration tester Kieran Smith meticulously dissected the firmware of an unbranded...
A clandestine pathway into the N-central server, bypassing all credential requirements, has once again been discovered, and this time, the vulnerability commands the absolute maximum severity rating. N-able has issued a dire warning regarding...
The pledge to return the lion’s share of the stolen bitcoin proved no mere bluff. The unknown parties who style themselves “white hats” sent 3,400 BTC, worth roughly $263 million, back to the Liquid...
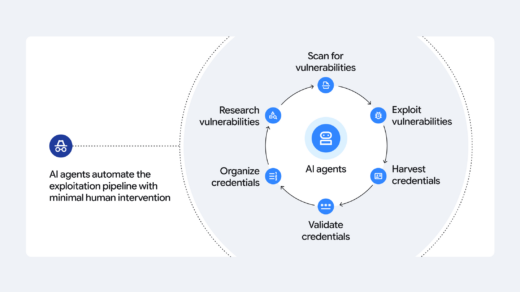
Artificial intelligence in attacks has ceased to be a mere accelerant for routine and has begun assuming entire segments of an operation. On September 8, the Google Threat Intelligence Group described the shift from...
The September Patch Tuesday became the largest security update release in Microsoft’s history. The company closed 966 vulnerabilities, two of which attackers had already wielded in real-world attacks. Previous records proved short-lived: in July,...
Photoshop has received an uncommonly weighty patch in which nearly every remediated flaw leads to the execution of foreign code. Adobe has released update APSB26-130 for Photoshop 2025 and 2026 on both Windows and...
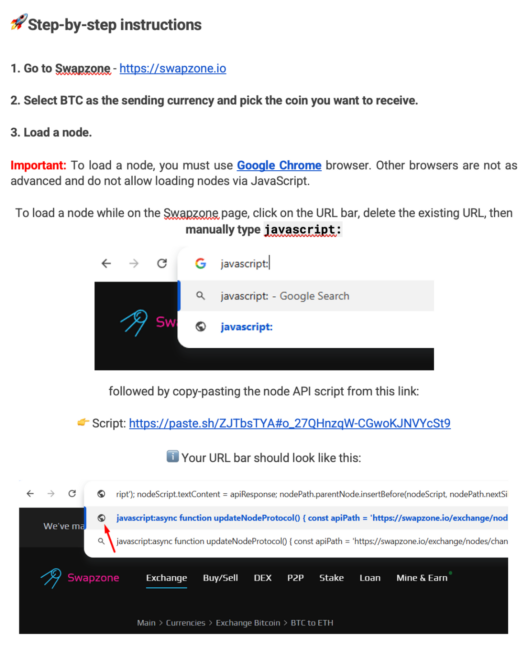
ClickFix has abandoned its habit of knocking at PowerShell and has taken up residence directly inside the browser. Cisco Talos has disclosed a campaign in which the victim is invited to paste JavaScript into...
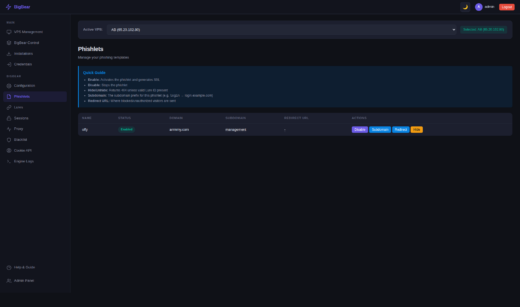
A user may enter the correct password, complete MFA verification, and still lose their Microsoft 365 account. The phishing platform BigBear 2.0 intercepts the authenticated session after the second factor and delivers the attacker...
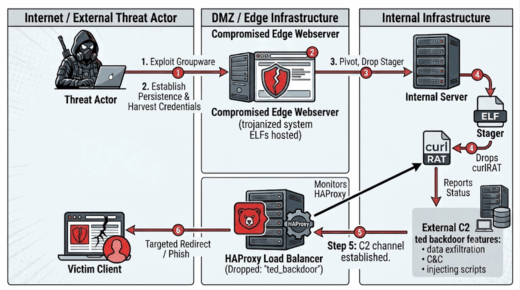
Suspected North Korean hackers may have spied on South Korean organizations for years using trojanized Linux system services and an HAProxy backdoor. Rapid7 researchers discovered a previously unknown set of malicious tools. These tools...
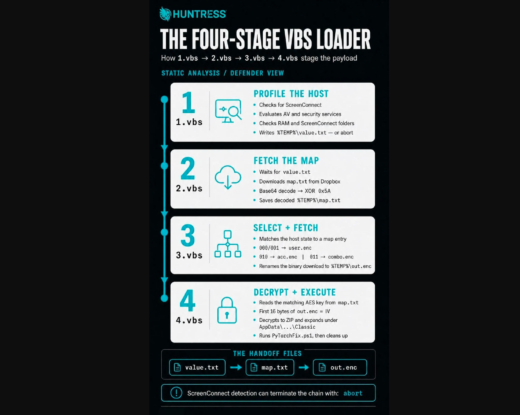
Cybercriminals have transformed ScreenConnect into a weaponized mechanism capable of infecting other ScreenConnect systems during standard connections. The modified client automatically detects a new session, dispatches malicious scripts via the native file transfer feature,...